

Question 21
Refer to the exhibit.
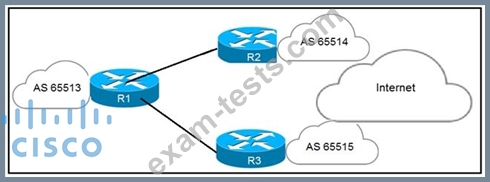
An engineer has successfully fixed BGP peering issue. R1 has an established eBGP peering with R2 and R3. Which mechanism should the engineer apply in order to steer the traffic correctly?
An engineer has successfully fixed BGP peering issue. R1 has an established eBGP peering with R2 and R3. Which mechanism should the engineer apply in order to steer the traffic correctly?
Question 22
For which reason can two devices fail to establish an OSPF neighbor relationship?
Question 23
Refer to the exhibit.

Refer to the exhibit After recent configuration changes to a customer's network, a network engineer notices that R2 cannot communicate with R3 Both FastEthemet interfaces on R2 and R3 are up and configured with the correct IP addresses MD5 password configured en R2 and R3 match with no issues What is the minimum change the engineer must make to enable R2 and R3 to communicate and fix the problem?
Refer to the exhibit After recent configuration changes to a customer's network, a network engineer notices that R2 cannot communicate with R3 Both FastEthemet interfaces on R2 and R3 are up and configured with the correct IP addresses MD5 password configured en R2 and R3 match with no issues What is the minimum change the engineer must make to enable R2 and R3 to communicate and fix the problem?
Question 24
What are two differences between OSPF and IS-IS? (Choose two.)
Question 25
Refer to the exhibit.

Refer to the exhibit. Company A established BGP sessions with several ISPs. A network engineer at the company must filter out all traffic except for routes that transit AS 152. The engineer configured the filtering policy "permit _152S_(_[0.9])" on R1, but after applying the configuration, the engineer notices that other routes are still visible. Which action resolves the issue?

Refer to the exhibit. Company A established BGP sessions with several ISPs. A network engineer at the company must filter out all traffic except for routes that transit AS 152. The engineer configured the filtering policy "permit _152S_(_[0.9])" on R1, but after applying the configuration, the engineer notices that other routes are still visible. Which action resolves the issue?