

Question 16
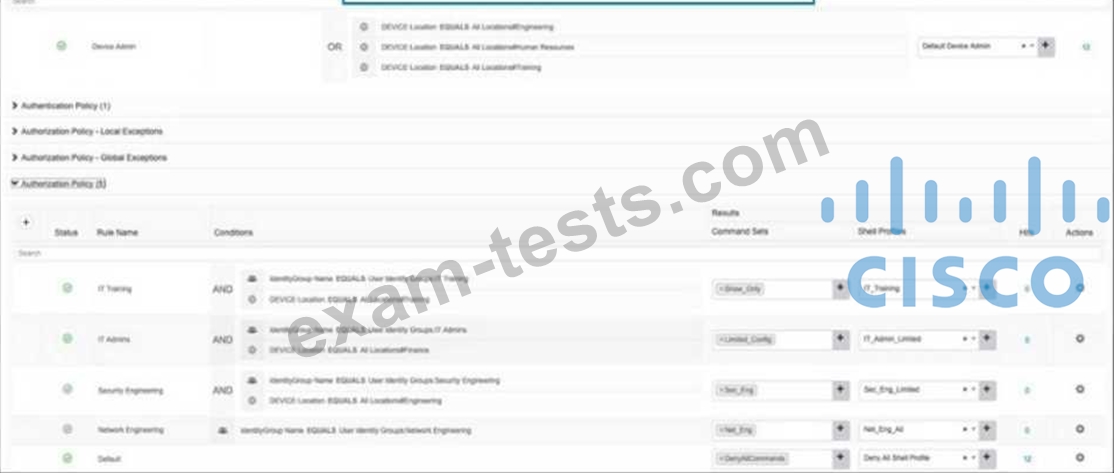
Refer to the exhibit. An organization recently implemented network device administration using Cisco ISE. Upon testing the ability to access all of the required devices, a user in the Cisco ISE group IT Admins is attempting to login to a device in their organization's finance department but is unable to. What is the problem?
Question 17
An administrator is attempting to replace the built-in self-signed certificates on a Cisco ISE appliance. The CA is requesting some information about the appliance in order to sign the new certificate. What must be done in order to provide the CA this information?
Question 18
A customer wants to set up the Sponsor portal and delegate the authentication flow to a third party for added security while using Kerberos Which database should be used to accomplish this goal?
Question 19
An organization has a fully distributed Cisco ISE deployment When implementing probes, an administrator must scan for unknown endpoints to learn the IP-to-MAC address bindings. The scan is complete on one FPSN. but the information is not available on the others. What must be done to make the information available?
Question 20
An administrator must authenticate Cisco Secure Client users by using a secure token against an LDAP server to grant wireless network access in a Cisco ISE deployment. These configurations have been performed:
* Configured Microsoft Active Directory as an external identity source
* Created an authentication policy
* Created an authorization policy
The administrator must create a Cisco Secure Client profile to complete the configuration. Which protocol must be implemented in the policy?
* Configured Microsoft Active Directory as an external identity source
* Created an authentication policy
* Created an authorization policy
The administrator must create a Cisco Secure Client profile to complete the configuration. Which protocol must be implemented in the policy?
Premium Bundle
Newest 300-715 Exam PDF Dumps shared by BraindumpsPass.com for Helping Passing 300-715 Exam! BraindumpsPass.com now offer the updated 300-715 exam dumps, the BraindumpsPass.com 300-715 exam questions have been updated and answers have been corrected get the latest BraindumpsPass.com 300-715 pdf dumps with Exam Engine here: