

Question 1
Identify the type of attack, an attacker is attempting on www.example.com website.

Question 2
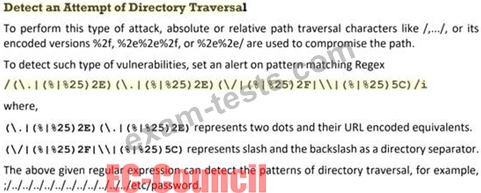
John, a SOC analyst, while monitoring and analyzing Apache web server logs, identified an event log matching Regex /(\.|(%|%25)2E)(\.|(%|%25)2E)(\/|(%|%25)2F|\\|(%|%25)5C)/i.
What does this event log indicate?
What does this event log indicate?
Question 3
According to the Risk Matrix table, what will be the risk level when the probability of an attack is very low and the impact of that attack is major?
Question 4
Ray is a SOC analyst in a company named Queens Tech. One Day, Queens Tech is affected by a DoS/DDoS attack. For the containment of this incident, Ray and his team are trying to provide additional bandwidth to the network devices and increasing the capacity of the servers.
What is Ray and his team doing?
What is Ray and his team doing?
Question 5
A type of threat intelligent that find out the information about the attacker by misleading them is known as
.
.