

Question 46
Jony, a security analyst, while monitoring IIS logs, identified events shown in the figure below.
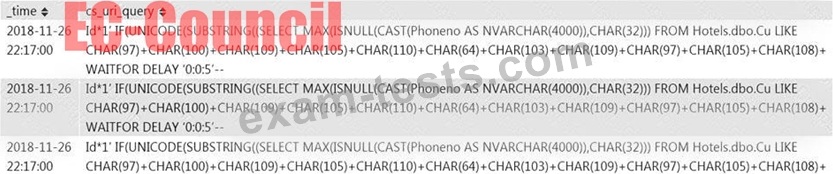
What does this event log indicate?
What does this event log indicate?
Question 47
John, a SOC analyst, while monitoring and analyzing Apache web server logs, identified an event log matching Regex /(\.|(%|%25)2E)(\.|(%|%25)2E)(\/|(%|%25)2F|\\|(%|%25)5C)/i.
What does this event log indicate?
What does this event log indicate?

Question 48
Which of the following can help you eliminate the burden of investigating false positives?
Question 49
Which of the following attack can be eradicated by disabling of "allow_url_fopen and allow_url_include" in the php.ini file?
Question 50
In which phase of Lockheed Martin's - Cyber Kill Chain Methodology, adversary creates a deliverable malicious payload using an exploit and a backdoor?
