

Question 46
You have an Azure subscription named Subcription1 that contains an Azure Active Directory (Azure AD) tenant named contosos.com and a resource group named RG1.
You create a custom role named Role1 for contoso.com.
You need to identify where you can use Role1 for permission delegation.
What should you identify?
You create a custom role named Role1 for contoso.com.
You need to identify where you can use Role1 for permission delegation.
What should you identify?
Question 47
You have an Azure subscription that contains an Azure SQL database named DB1 in the East US Azure region. You create the storage accounts shown in the following table.
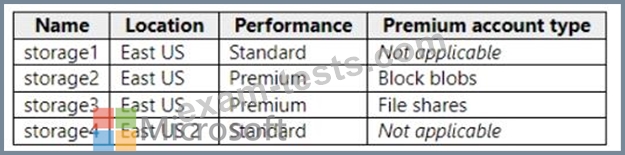
You plan to enable auditing for DB1.
Which storage accounts can you use as the auditing destination for DB1?
You plan to enable auditing for DB1.
Which storage accounts can you use as the auditing destination for DB1?
Question 48
You have an Azure Active Directory (Azure AD) tenant and a root management group.
You create 10 Azure subscriptions and add the subscriptions to the rout management group.
You need to create an Azure Blueprints definition that will be stored in the root management group.
What should you do first?
You create 10 Azure subscriptions and add the subscriptions to the rout management group.
You need to create an Azure Blueprints definition that will be stored in the root management group.
What should you do first?
Question 49
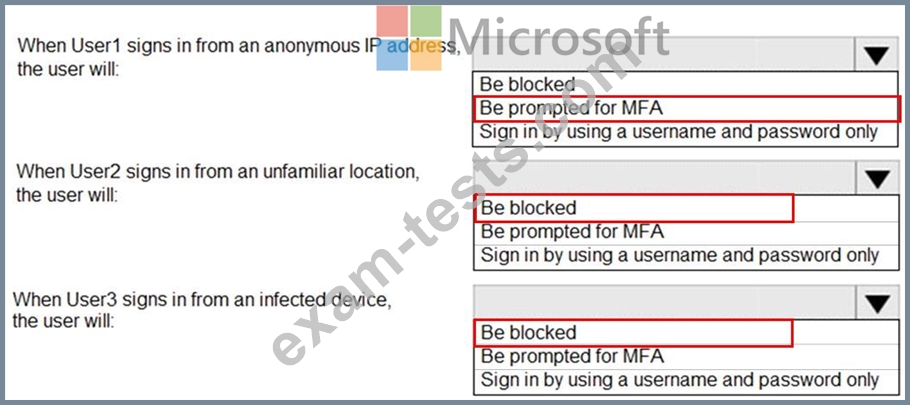
You have an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.

You create and enforce an Azure AD Identity Protection sign-in risk policy that has the following settings:
Assignments: Include Group1, exclude Group2
Conditions: Sign-in risk level: Medium and above
Access Allow access, Require multi-factor authentication
You need to identify what occurs when the users sign in to Azure AD.
What should you identify for each user? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question 50
You have an Azure subscription that contains an Azure SQL database named SQL1 and an Azure key vault named KeyVault1. KeyVault1 stores the keys shown in the following table.

You reed to configure Transparent Data Encryption (TDE). TDE will use a customer-managed key for SQL1?
You reed to configure Transparent Data Encryption (TDE). TDE will use a customer-managed key for SQL1?
Premium Bundle
Newest AZ-500 Exam PDF Dumps shared by BraindumpsPass.com for Helping Passing AZ-500 Exam! BraindumpsPass.com now offer the updated AZ-500 exam dumps, the BraindumpsPass.com AZ-500 exam questions have been updated and answers have been corrected get the latest BraindumpsPass.com AZ-500 pdf dumps with Exam Engine here: