

Question 11
You have an Azure Sentinel workspace that has an Azure Active Directory (Azure AD) data connector.
You are threat hunting suspicious traffic from a specific IP address.
You need to annotate an intermediate event stored in the workspace and be able to reference the IP address when navigating through the investigation graph.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

Question 12
On Monday, you configure an email notification in Azure Security Center to notify user [email protected].
On Tuesday, Security Center generates the security alerts shown in the following table.
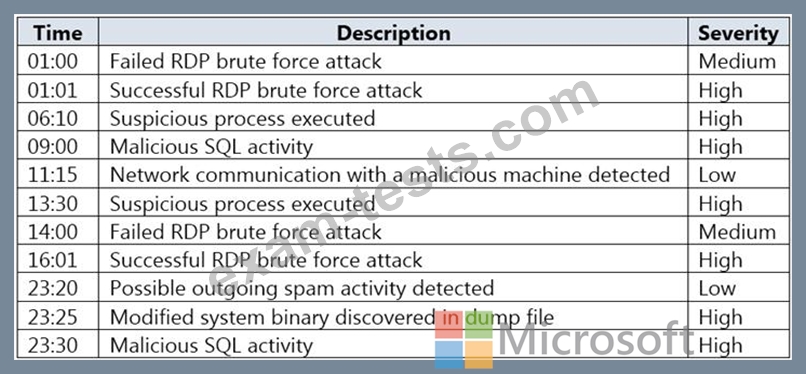
How many email notifications will [email protected] receive on Tuesday? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

On Tuesday, Security Center generates the security alerts shown in the following table.
How many email notifications will [email protected] receive on Tuesday? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Question 13
You have an Azure subscription that contains the resources shown in the following table.

The subscription is linked to an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.

You create the groups shown in the following table.

The membership rules for Group1 and Group2 are configured as shown in the following exhibit.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

The subscription is linked to an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.
You create the groups shown in the following table.
The membership rules for Group1 and Group2 are configured as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Question 14
You have an Azure environment.
You need to identify any Azure configurations and workloads that are non-compliant with ISO 27001:2013 standards.
What should you use?
You need to identify any Azure configurations and workloads that are non-compliant with ISO 27001:2013 standards.
What should you use?
Question 15
You have an Azure subscription that contains the users shown in the following table.

Which users can enable Azure AD Privileged Identity Management (PIM)?
Which users can enable Azure AD Privileged Identity Management (PIM)?