

Question 66
A company'sSIEMis designed to associate the company'sasset inventorywith user events. Given the following report:
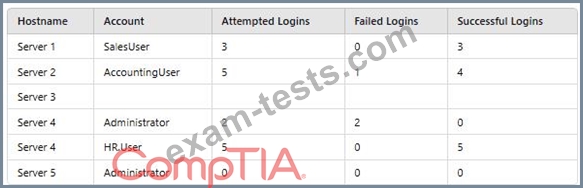
Which of thefollowing should asecurity engineer investigate firstas part of alog audit?
Which of thefollowing should asecurity engineer investigate firstas part of alog audit?
Question 67
A company updates its cloud-based services by saving infrastructure code in a remote repository.
The code is automatically deployed into the development environment every time the code is saved to the repository. The developers express concern that the deployment often fails, citing minor code issues and occasional security control check failures in the development environment.
Which of the following should a security engineer recommend to reduce the deployment failures?
(Choose two.)
Question 68
A vulnerability can on a web server identified the following:
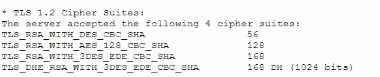
Which of the following actions would most likely eliminate on path decryption attacks? (Select two).
Which of the following actions would most likely eliminate on path decryption attacks? (Select two).
Question 69
A security engineer reviews an after action report from a previous security breach and notes a long lag time between detection and containment of a compromised account. The engineer suggests using SOAR to address this concern. Which of the following best explains the engineer's goal?
Question 70
A security engineer is reviewing event logs because an employee successfully connected a personal Windows laptop to the corporate network, which is against company policy. Company policy allows all Windows 10 and 11 laptops to connect to the system as long as the MDM agent installed by IT is running. Only compliant devices can connect, and the logic in the system to evaluate compliant laptops is as follows:
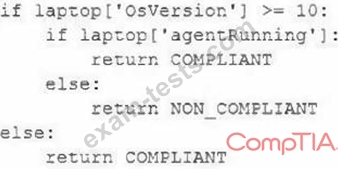
Which of the following most likely occurred when the employee connected a personally owned Windows laptop and was allowed on the network?
Which of the following most likely occurred when the employee connected a personally owned Windows laptop and was allowed on the network?