

Question 191
During a security assessment using an EDR solution, a security engineer generates the following report about the assets in the system:
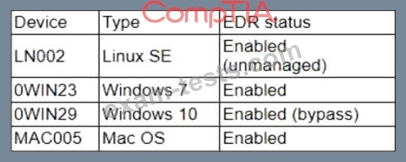
After five days, the EDR console reports a blocked infection on the host 0WIN23 by a remote access Trojan. Which of the following most likely enabled the attempted infection?
After five days, the EDR console reports a blocked infection on the host 0WIN23 by a remote access Trojan. Which of the following most likely enabled the attempted infection?
Question 192
The material findings from a recent compliance audit indicate a company has an issue with excessive permissions. The findings show that employees changing roles or departments results in privilege creep. Which of the following solutions are the best ways to mitigate this issue?
(Choose two.)
(Choose two.)
Question 193
A senior security engineer flags the following log file snippet as having likely facilitated an attacker's lateral movement in a recent breach:
qry_source: 19.27.214.22 TCP/53
qry_dest: 199.105.22.13 TCP/53
qry_type: AXFR
| in comptia.org
------------ directoryserver1 A 10.80.8.10
------------directoryserver2 A 10.80.8.11
------------ directoryserver3 A 10.80.8.12
------------ internal-dns A 10.80.9.1
----------- www-int A 10.80.9.3
------------ fshare A 10.80.9.4
------------ sip A 10.80.9.5
------------ msn-crit-apcs A 10.81.22.33
Which of the following solutions, if implemented, would mitigate the risk of this issue reoccurring?
Question 194
A company lined an email service provider called my-email.com to deliver company emails. The company stalled having several issues during the migration. A security engineer is troubleshooting and observes the following configuration snippet:
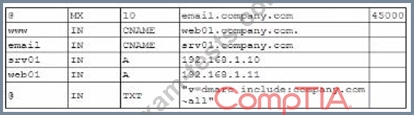
Which of the following should the security engineer modify to fix the issue? (Select two).
Which of the following should the security engineer modify to fix the issue? (Select two).
Question 195
A security engineer needs 10 secure the OT environment based on me following requirements:
- Isolate the OT network segment
- Restrict Internet access.
- Apply security updates two workstations
- Provide remote access to third-party vendors
Which of the following design strategies should the engineer implement to best meet these requirements?
- Isolate the OT network segment
- Restrict Internet access.
- Apply security updates two workstations
- Provide remote access to third-party vendors
Which of the following design strategies should the engineer implement to best meet these requirements?