

Question 276
A DNS forward lookup zone named comptia.org must:
- Ensure the DNS is protected from on-path attacks.
- Ensure zone transfers use mutual authentication and are authenticated and negotiated.
Which of the following should the security architect configure to meet these requirements?
(Choose two).
- Ensure the DNS is protected from on-path attacks.
- Ensure zone transfers use mutual authentication and are authenticated and negotiated.
Which of the following should the security architect configure to meet these requirements?
(Choose two).
Question 277
A security engineer added a new server to the company email cluster. The server has a new external IP address associated with it. After a few days, the service desk started receiving complaints from users about their outgoing messages to customers being flagged as spam.
Which of the following records should the security engineer update to fix the issue? (Choose two.)
Which of the following records should the security engineer update to fix the issue? (Choose two.)
Question 278
Several unlabeled documents in a cloud document repository contain cardholder information.
Which of the following configuration changes should be made to the DLP system to correctly label these documents in the future?
Which of the following configuration changes should be made to the DLP system to correctly label these documents in the future?
Question 279
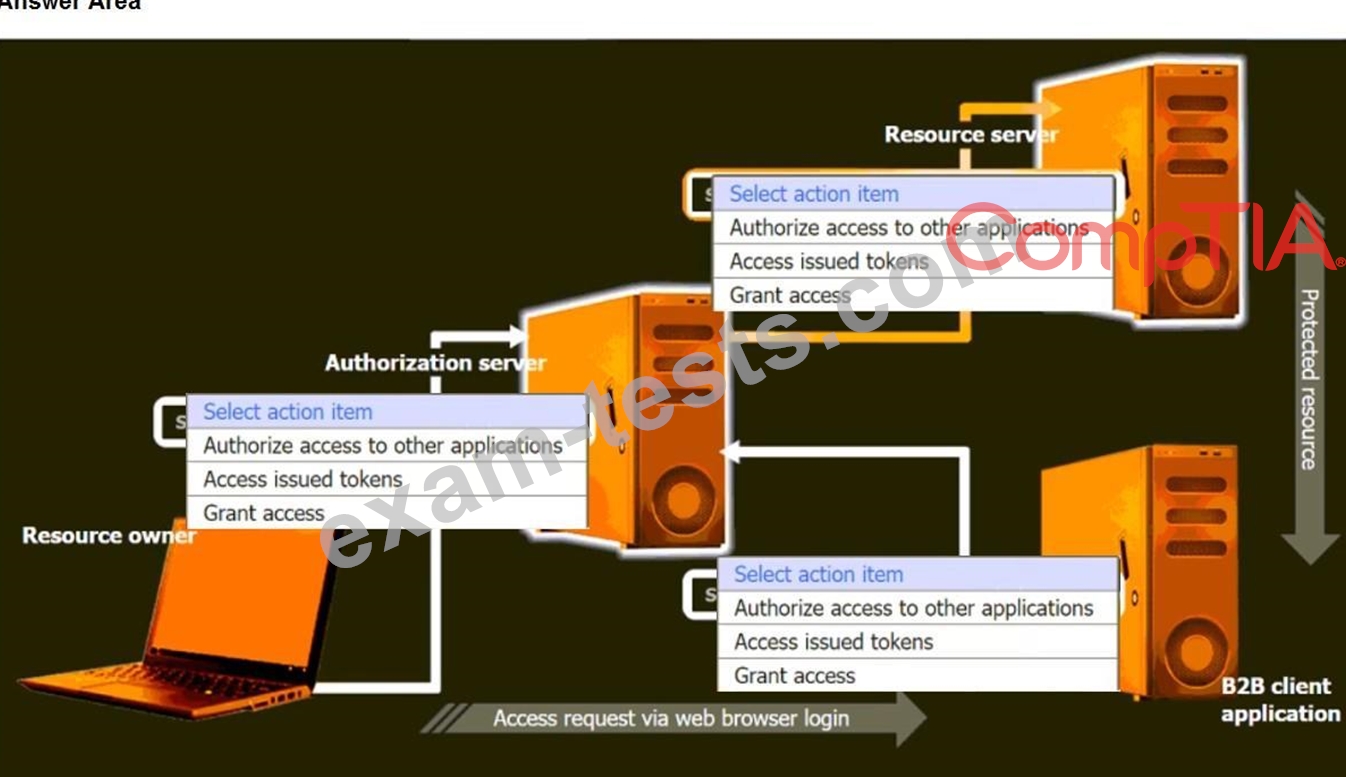
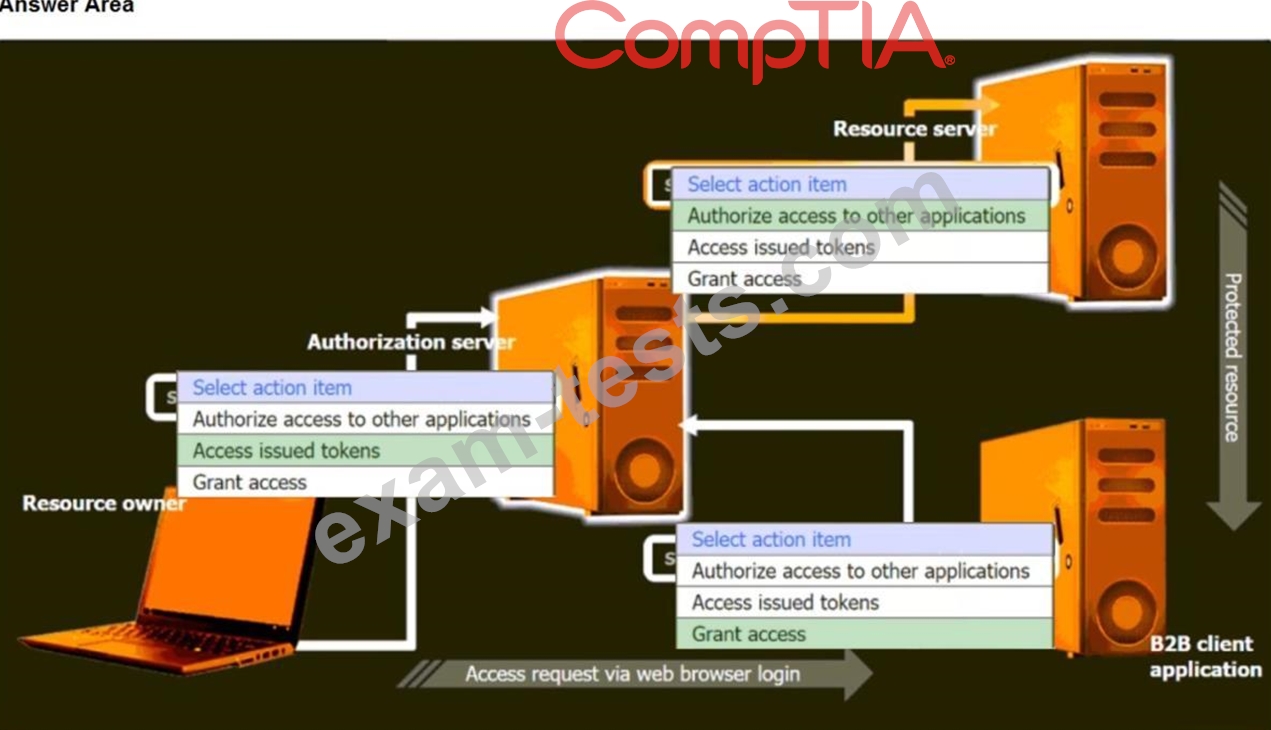
SIMULATION
You are tasked with integrating a new B2B client application with an existing OAuth workflow that must meet the following requirements:
- The application does not need to know the users' credentials.
- An approval interaction between the users and the HTTP service must be orchestrated.
- The application must have limited access to users' data.
INSTRUCTIONS
Use the drop-down menus to select the action items for the appropriate locations. All placeholders must be filled.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
You are tasked with integrating a new B2B client application with an existing OAuth workflow that must meet the following requirements:
- The application does not need to know the users' credentials.
- An approval interaction between the users and the HTTP service must be orchestrated.
- The application must have limited access to users' data.
INSTRUCTIONS
Use the drop-down menus to select the action items for the appropriate locations. All placeholders must be filled.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Question 280
A security architect discovers the following while reviewing code for a company's website:
selection = "SELECT Item FROM Catalog WHERE ItemID = " &
Request("ItemID")
Which of the following should the security architect recommend?
selection = "SELECT Item FROM Catalog WHERE ItemID = " &
Request("ItemID")
Which of the following should the security architect recommend?