

Question 36
A security analyst is reviewing the following event timeline from an COR solution:
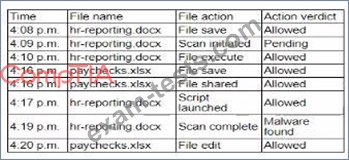
Which of the following most likely has occurred and needs to be fixed?
Which of the following most likely has occurred and needs to be fixed?
Question 37
After an organization met with its ISAC, the organization decided to test the resiliency of its security controls against a small number of advanced threat actors. Which of the following will enable the security administrator to accomplish this task?
Question 38
A software development team requires valid data for internal tests. Company regulations, however do not allow the use of this data in cleartext. Which of the following solutions best meet these requirements?
Question 39
Which of the following best explains the business requirement a healthcare provider fulfills by encrypting patient data at rest?
Question 40
An organization is looking for gaps in its detection capabilities based on the APTs that may target the industry Which of the following should the security analyst use to perform threat modeling?