

Question 501
When should a post-mortem review meeting be held after an intrusion has been properly taken care of?
Question 502
Who would be the BEST person to approve an organizations information security policy?
Question 503
What type of investigation applies when malicious behavior is suspected between two organizations?
Question 504
Which of the following is of GREATEST value to an organization in which information security controls are perceived as complex and negatively impacting productivity
Question 505
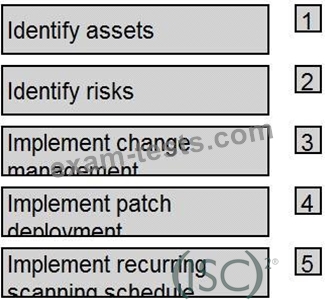
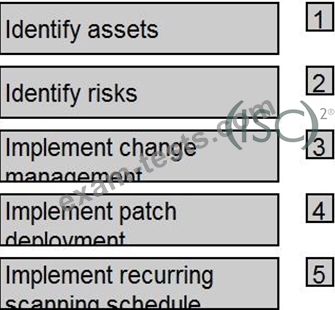
Order the below steps to create an effective vulnerability management process.
Premium Bundle
Newest CISSP Exam PDF Dumps shared by BraindumpsPass.com for Helping Passing CISSP Exam! BraindumpsPass.com now offer the updated CISSP exam dumps, the BraindumpsPass.com CISSP exam questions have been updated and answers have been corrected get the latest BraindumpsPass.com CISSP pdf dumps with Exam Engine here: