Exhibit. Refer to the exhibit, which shows the output of get system ha status. NGFW-1 and NGFW-2 have been up for a week. Which two statements about the output are true? (Choose two.)
Correct Answer: B,C
* FortiGate HA Troubleshooting and Synchronization Guides * Fortinet Admin Guide: HA Primary Role Retention, Cluster Break-up Due to Out-of-Sync Status
Question 107
Exhibit. Refer to the exhibit, which contains partial output from an IKE real-time debug. Which two statements about this debug output are correct? (Choose two.)
Correct Answer: C,D
From the exhibit, you can observe that the debug output captures an IKEv1 negotiation in aggressive mode. Let ' s break down the supporting details in line with official Fortinet IPsec VPN troubleshooting resources and debug guides: For Option B: The very first line of the debug output shows: comes 10.0.0.2:500- > 10.0.0.1:500, ifindex=7. This indicates the traffic direction-from the remote IP (10.0.0.2) with port 500 to the local IP (10.0.0.1) with port 500. According to Fortinet ' s documentation, the right side of the arrow always represents the local FortiGate gateway. Thus, 10.0.0.1 is the local gateway IP address. For Option D: You see the statement: negotiation result " remote " and received peer identifier FQDNCE88525E7DE7F00D6C2D3C00000000 Official debug documentation describes that the " peer identifier " or peer ID sent by the initiator is displayed here. In the context of IKE/IPsec negotiation, this value is used as the IPsec peer ID for authentication and identification purposes. The initiator is providing " remote " as the peer ID for its connection. Why Not A or C: Perfect Forward Secrecy (PFS): The debug does not show any DH group negotiation in phase 2 (no reference to group2, group5, etc., for phase 2), so you cannot deduce the presence of PFS solely from this output. Phase 2 negotiation: The log focuses on IKE (phase 1) negotiation and establishment; there's no reference to ESP protocol, Quick Mode, or other identifiers that would show phase 2 SA negotiation and establishment. This interpretation aligns with the explanation in the FortiOS 7.6.4 Administration Guide ' s VPN section and the official debug command output samples published in Fortinet's documentation. It demonstrates how to distinguish between local and remote addresses and how to identify the use of peer IDs. References: FortiOS 7.6.4 Administration Guide: IPsec VPN and Debugging VPNs Technical Support Resources on interpreting IKE debug output and peer ID roles
Question 108
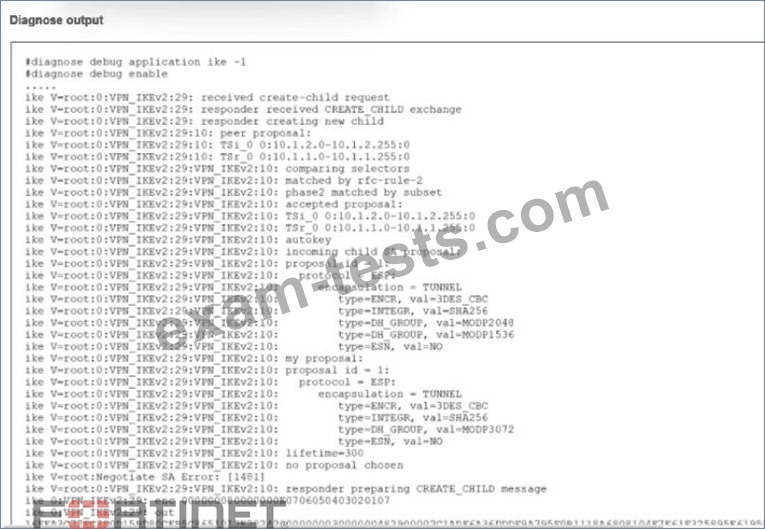
Refer to the exhibit. An IPsec VPN tunnel using IKEv2 was brought up successfully, but when the tunnel rekey takes place the tunnel goes down. The debug command for IKE was enabled and, in the exhibit, you can review the partial output of the debug IKE while attempting to bring the tunnel up. What is causing. The tunnel to be down?
Correct Answer: A
To determine the cause of the failure, we must analyze the IKEv2 debug output provided in the exhibit (image_ad3dc6.jpg): Identify the Negotiation Phase: The debug log shows: responder received CREATE_CHILD exchange. In IKEv2, the CREATE_CHILD_SA exchange is used to create new Child SAs (Phase 2) or to rekey existing ones. The fact that the tunnel was previously "brought up successfully" implies the initial IKE SA (Phase 1) is stable, and this error is occurring specifically during a rekey event, which often involves Perfect Forward Secrecy (PFS). Analyze the Proposals (The Mismatch): Incoming Proposal (Remote Peer): The remote peer sends a proposal containing two Diffie-Hellman groups: type=DH_GROUP, val=MODP2048 (Group 14) and type=DH_GROUP, val=MODP1536 (Group 5). My Proposal (Local FortiGate): The local FortiGate configuration expects: type=DH_GROUP, val=MODP3072 (Group 15). Result of the Negotiation: The debug output concludes with: no proposal chosen and Negotiate SA Error. This error occurs because the local FortiGate cannot find a common Diffie-Hellman group between what it requires (Group 15) and what the peer is offering (Groups 14 or 5). While this is technically a mismatch occurring during the Phase 2 (Child SA) creation, "A Diffie-Hellman mismatch" (Option A) is the precise root cause identified in the logs. Why other options are incorrect: B: The log shows received create-child request, confirming that UDP traffic is reaching the device and is not blocked. C: The failure is in the CREATE_CHILD exchange (Phase 2/Rekey), not the IKE_SA_INIT or IKE_AUTH (Phase 1) exchanges. D: While the mismatch is occurring within the Phase 2 definitions, Option A is the specific technical reason for the no proposal chosen error shown in the DH_GROUP lines. Reference: FortiGate Security 7.6 Study Guide (IPsec VPN): "Phase 2 parameters... if Perfect Forward Secrecy (PFS) is enabled, a Diffie-Hellman exchange is performed again. Both peers must match the DH Group."
Question 109
What is the diagnose test application ipsmonitor 5 command used for? (Choose one answer)
Correct Answer: B
Question 110
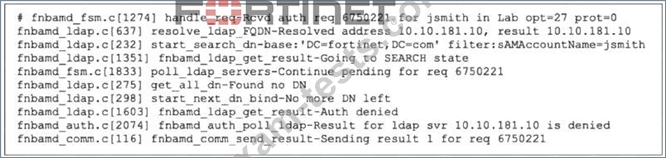
Refer to the exhibit, which shows a partial output of the real-time LDAP debug. What two actions can the administrator take to resolve this issue? (Choose two.)