Question 86
You want only his telnet stream to be able to access the server (address 1011.100). Then, you add the following ACL to the routing ring: nule5pemit cp source ny destination 1011.100000destination-porteq 23 rule
1l0 deny ip source any destination any Then you apply that ACL to the ingress direction of the router's seial interface. What type of message is allowed to pass through the router?( Multiple choice questions).
1l0 deny ip source any destination any Then you apply that ACL to the ingress direction of the router's seial interface. What type of message is allowed to pass through the router?( Multiple choice questions).
Question 87
The following statement about the application of BFD is correct?
Question 88
The LSA of type certainly does not exist in the 2
Question 89
Regarding BGP4+, the following statement is correct?
Question 90
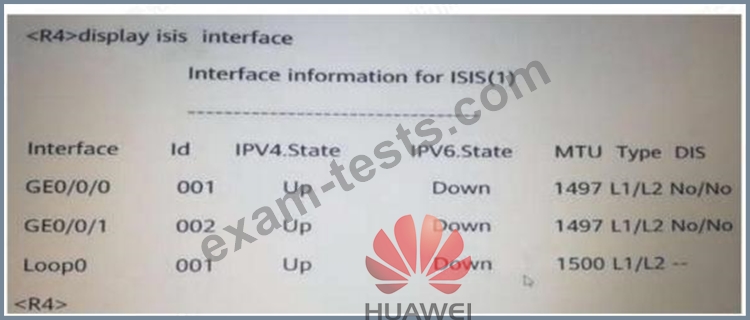
Based on the configuration shown in the figure below, it can be known that R4 has () interfaces advertised into IS-IS?