

Question 21
You have a Microsoft 365 E5 tenant that contains 100 Windows 10 devices.
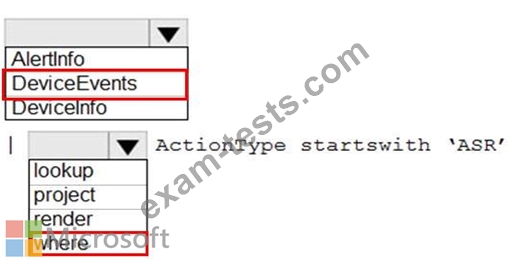
You plan to attack surface reduction (ASR) rules for the Windows 10 devices.
You configure the ASR rules in audit mode and collect audit data in a Log Analytics workspace.
You need to find the ASR rules that match the activities on the devices.
How should you complete the Kusto query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question 22
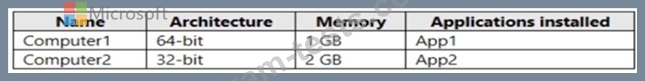
You have 100 computers that run Windows 8.1 and are enrolled in Upgrade Readiness.
Two of the computers are configured as shown in the following table.
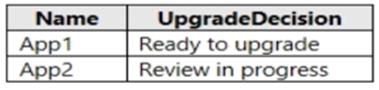
From Upgrade Readiness, you view the applications shown in the following table.
You enroll a computer named Computer3 in Upgrade Readiness. Computer3 has the following configurations:
* 8 GB of memory
* 64-bit architecture
* An application named App3 installed
App3 is installed on Computer3 only.
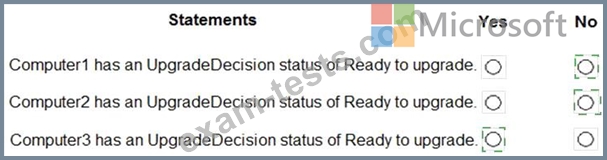
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Two of the computers are configured as shown in the following table.
From Upgrade Readiness, you view the applications shown in the following table.
You enroll a computer named Computer3 in Upgrade Readiness. Computer3 has the following configurations:
* 8 GB of memory
* 64-bit architecture
* An application named App3 installed
App3 is installed on Computer3 only.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Question 23
Your company uses Microsoft Cloud App Security.
You plan to integrate Cloud App Security and security information and event management (SIEM).
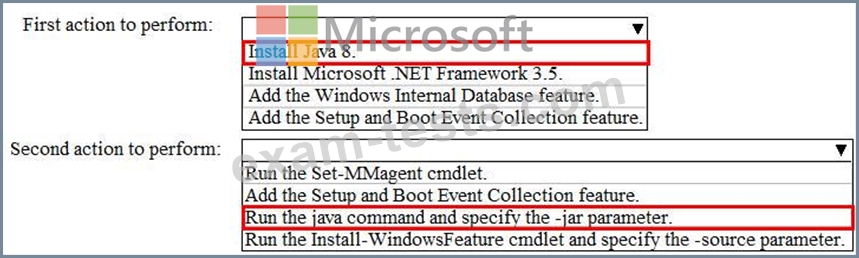
You need to deploy a SIEM agent on a server that runs Windows Server 2016.
What should you do? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
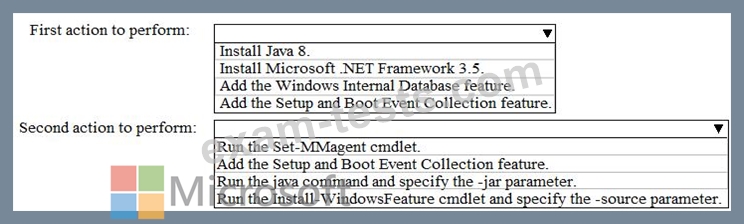
You plan to integrate Cloud App Security and security information and event management (SIEM).
You need to deploy a SIEM agent on a server that runs Windows Server 2016.
What should you do? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Question 24
You have a Microsoft 365 E5 tenant that contains the users shown in the following table.

You provision the private store in Microsoft Store for Business.
You assign Microsoft Store for Business roles to the users as shown in the following table.

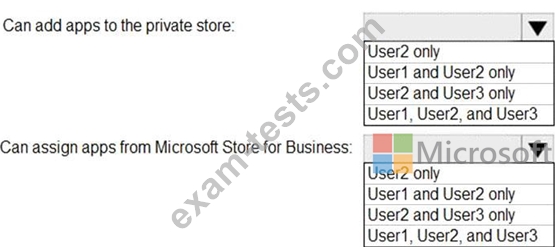
You need to identify which users can add apps to the private store, and which users can assign apps from Microsoft Store for Business.
Which users should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You provision the private store in Microsoft Store for Business.
You assign Microsoft Store for Business roles to the users as shown in the following table.
You need to identify which users can add apps to the private store, and which users can assign apps from Microsoft Store for Business.
Which users should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Question 25
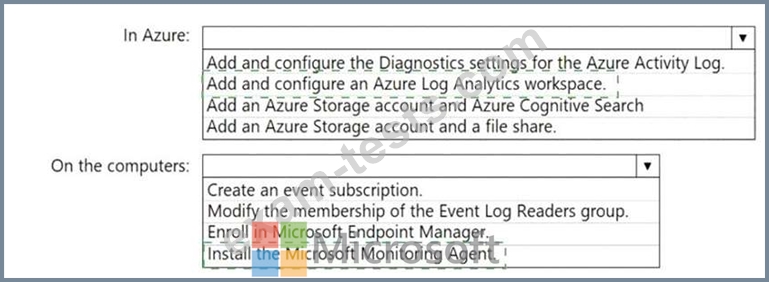
Your company has five security information and event management (SIEM) appliances. The traffic logs from each appliance are saved to a file share named Logs.
You need to analyze the traffic logs.
What should you do from Microsoft Cloud App Security?
You need to analyze the traffic logs.
What should you do from Microsoft Cloud App Security?