

Question 246
You are a penetration tester running port scans on a server.
INSTRUCTIONS
Part 1: Given the output, construct the command that was used to generate this output from the available options.
Part 2: Once the command is appropriately constructed, use the given output to identify the potential attack vectors that should be investigated further.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Question 247
A penetration tester has obtained a low-privilege shell on a Windows server with a default configuration and now wants to explore the ability to exploit misconfigured service permissions. Which of the following commands would help the tester START this process?
Question 248
Penetration tester has discovered an unknown Linux 64-bit executable binary. Which of the following tools would be BEST to use to analyze this issue?
Question 249
A penetration tester performs the following command:
curl -I -http2 https://www.comptia.org
Which of the following snippets of output will the tester MOST likely receive?
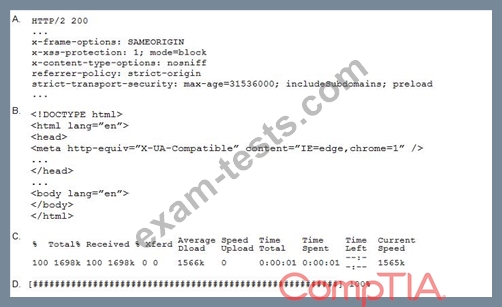
curl -I -http2 https://www.comptia.org
Which of the following snippets of output will the tester MOST likely receive?
Question 250
During an assessment, a penetration tester found a suspicious script that could indicate a prior compromise.
While reading the script, the penetration tester noticed the following lines of code:

Which of the following was the script author trying to do?
While reading the script, the penetration tester noticed the following lines of code:
Which of the following was the script author trying to do?