

Question 251
You have a Microsoft 365 tenant named contoso.com.
Guest user access is enabled.
Users are invited to collaborate with contoso.com as shown in the following table.

From the External collaboration settings in the Azure Active Directory admin center, you configure the Collaboration restrictions settings as shown in the following exhibit.

From a Microsoft SharePoint Online site, a user invites [email protected] to the site.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Guest user access is enabled.
Users are invited to collaborate with contoso.com as shown in the following table.
From the External collaboration settings in the Azure Active Directory admin center, you configure the Collaboration restrictions settings as shown in the following exhibit.
From a Microsoft SharePoint Online site, a user invites [email protected] to the site.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.


Question 252
You have an Azure AD tenant that contains the users shown in the following table.
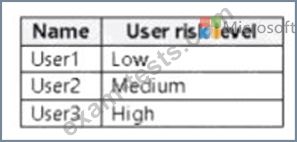
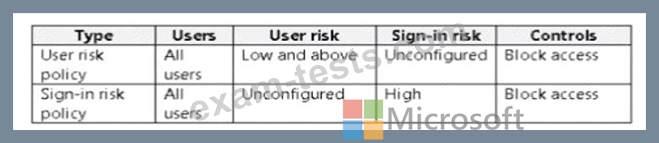
You have the Azure AD Identity Protection policies shown in the following table.
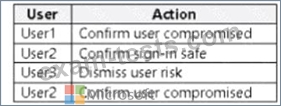
You review the Risky users report and the Risky sign-ins report and perform actions for each user as shown in the following table.
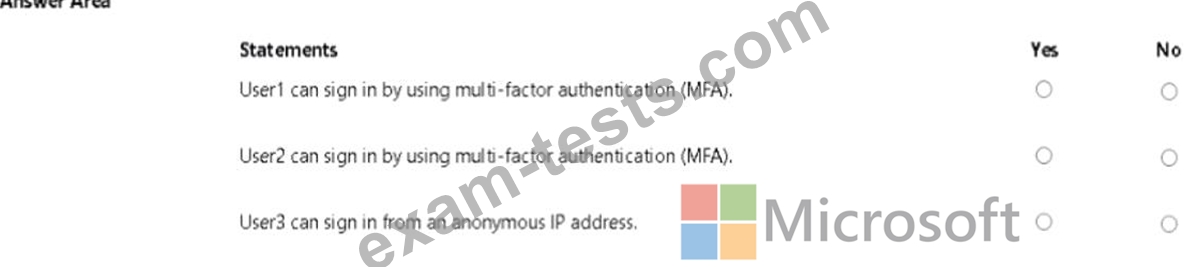
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You have the Azure AD Identity Protection policies shown in the following table.
You review the Risky users report and the Risky sign-ins report and perform actions for each user as shown in the following table.
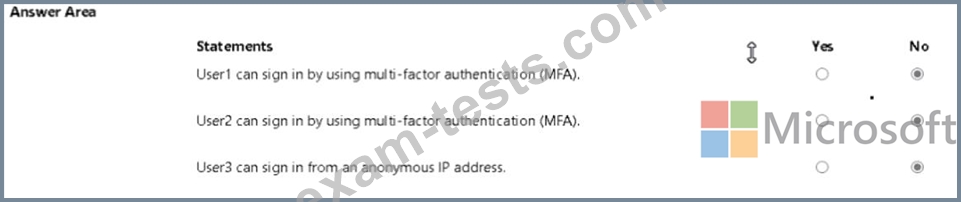
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Question 253
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it as a result, these questions will not appear in the review screen.
You have an Amazon Web Services (AWS) account, a Google Workspace subscription, and a GitHub account.
You deploy an Azure subscription and enable Microsoft 365 Defender.
You need to ensure that you can monitor OAuth authentication requests by using Microsoft Defender for Cloud Apps.
Solution: From the Microsoft 365 Defender portal, you add the Google Workspace app connector.
Does this meet the goal?
Question 254
Your network contains an on-premises Active Directory domain that syncs to an Azure Active Directory (Azure AD) tenant.
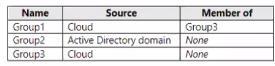
The tenant contains the groups shown in the following table.
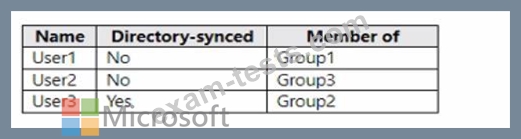
The tenant contains the users shown in the following table.
You create an access review as shown in the following table.
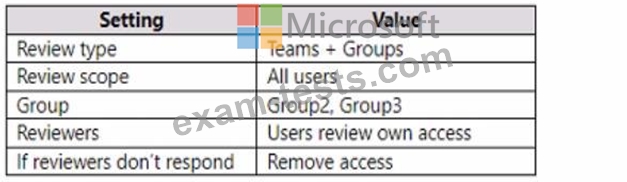
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

The tenant contains the groups shown in the following table.
The tenant contains the users shown in the following table.
You create an access review as shown in the following table.
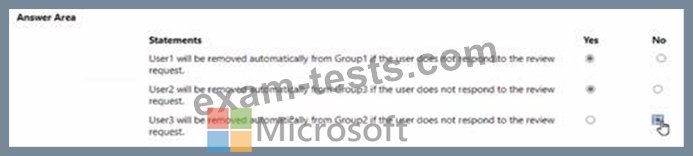
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Question 255
Your company recently implemented Azure Active Directory (Azure AD) Privileged Identity Management (PIM).
While you review the roles in PIM, you discover that all 15 users in the IT department at the company have permanent security administrator rights.
You need to ensure that the IT department users only have access to the Security administrator role when required.
What should you configure for the Security administrator role assignment?