

Question 36
What should a security engineer prioritize when building a new security process?
Question 37
An engineer is examining a correlation search as a part of a detection review, and sees that it is configured in the following fashion:
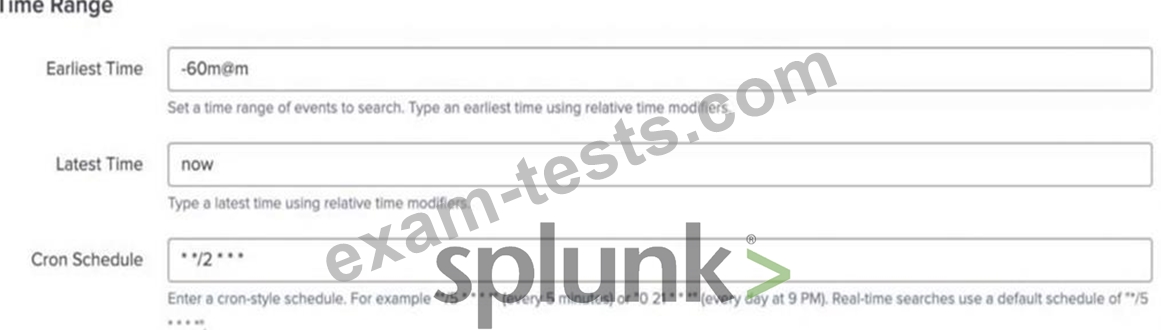
Which of the following is true about this configuration?
Which of the following is true about this configuration?
Question 38
The SOC notices over the course of an investigation there are numerous logs like the following:
14-Apr-2024 20:16:49.083 client 15.111.116.918*18345 UDP: query:
reallybad.c2.com IN A response: SERVFAIL +E
What detection should be created to alert on this behavior for the future?
14-Apr-2024 20:16:49.083 client 15.111.116.918*18345 UDP: query:
reallybad.c2.com IN A response: SERVFAIL +E
What detection should be created to alert on this behavior for the future?
Question 39
In Enterprise Security, what is the name of the threat intelligence lookup pertaining to files?
Question 40
Lookups append fields from an external source to events based on the values of fields that are already present in those events. What are the four supported lookup types?