

Question 106
A key feature of Cortex XSIAM Playbooks is their ability to leverage context from incidents and indicators. An incident is triggered based on a 'Rare Login from New Geo' alert. The associated playbook needs to: 1) Enrich the incident with user HR data (e.g., department, manager), 2) Check if the user is currently on approved travel to that geo, and 3) If not, initiate a multi-factor authentication (MFA) challenge. Which of the following code snippets and conceptual approaches correctly illustrate how to achieve the enrichment and conditional MFA challenge within a Cortex XSIAM Playbook, assuming appropriate integrations are configured?
Question 107
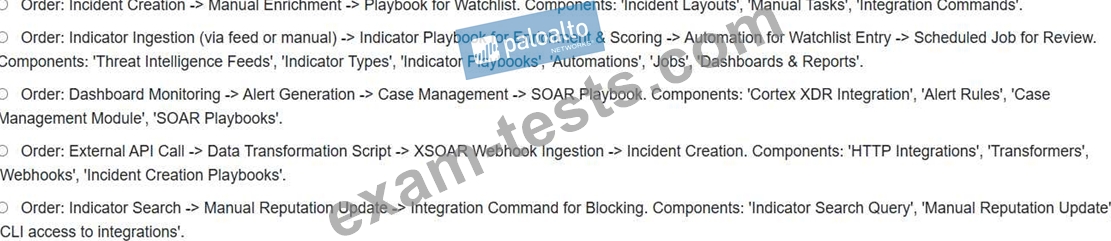
A SOC needs to establish a robust process in Cortex XSOAR for handling newly identified malicious domains. This process must include: 1) Automatic enrichment from multiple public and private sources. 2) A confidence score assignment based on the number of sources flagging the domain. 3) Automatic creation of a 'watchlist' entry for security devices if the confidence score exceeds a certain threshold. 4) A periodic review mechanism for domains that remain in the watchlist for an extended period without new activity. Which XSOAR components and configurations are essential to implement this entire workflow, and what is the typical order of operations?
Question 108
A sophisticated attacker has gained initial access to a corporate network and is attempting to establish persistence. They use a less common technique: modifying a legitimate scheduled task to execute a malicious script at logon, but they are careful not to create a new task or change the task's name significantly. Cortex XDR's default behavioral analytics successfully detects and prevents this. Which specific behavioral analytics capability, relying on the 'event of interest' concept and a 'sequence of events', is most effective here, and why is it superior to traditional signature-based methods?
Question 109
A sophisticated adversary has managed to establish persistence on an internal server within an organization monitored by Cortex XSIAM, bypassing initial preventative controls. The XSIAM platform has generated an alert for 'Suspicious PowerShell Execution'. As a Tier 2 SOC analyst, you need to conduct a deeper investigation. Which combination of XSIAM capabilities and data artifacts would provide the most comprehensive understanding of the persistence mechanism and lateral movement attempts?
Question 110
A customer is investigating a security incident in which unusual network traffic is observed and a malicious process is identified on an endpoint. Which Cortex XDR capability assists with correlating firewall network logs and endpoint data in this environment?