

Question 271
During which phase of the forensic process is data that is related to a specific event labeled and recorded to preserve its integrity?
Question 272
Which of these describes SOC metrics in relation to security incidents?
Question 273
The SOC team has confirmed a potential indicator of compromise on an endpoint. The team has narrowed the executable file's type to a new trojan family. According to the NIST Computer Security Incident Handling Guide, what is the next step in handling this event?
Question 274
Refer to the exhibit.
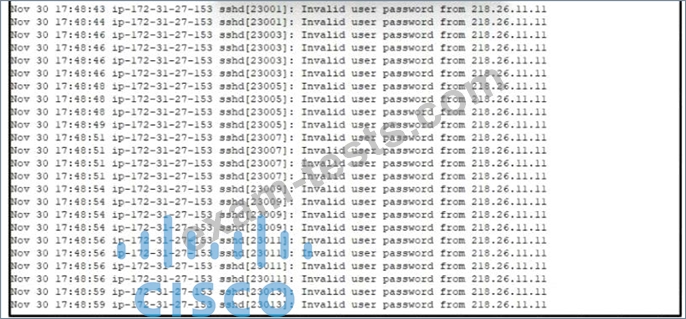
A security analyst is investigating unusual activity from an unknown IP address Which type of evidence is this file1?
A security analyst is investigating unusual activity from an unknown IP address Which type of evidence is this file1?
Question 275
Which type of verification consists of using tools to compute the message digest of the original and copied data, then comparing the similarity of the digests?