Question 51
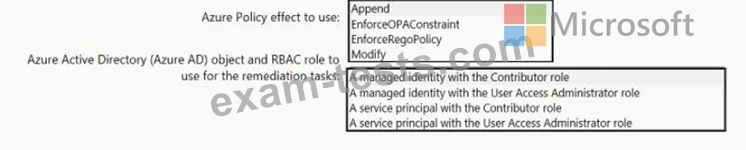
You need to design an Azure policy that will implement the following functionality:
* For new resources, assign tags and values that match the tags and values of the resource group to which the resources are deployed.
* For existing resources, identify whether the tags and values match the tags and values of the resource group that contains the resources.
* For any non-compliant resources, trigger auto-generated remediation tasks to create missing tags and values.
The solution must use the principle of least privilege.
What should you include in the design? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
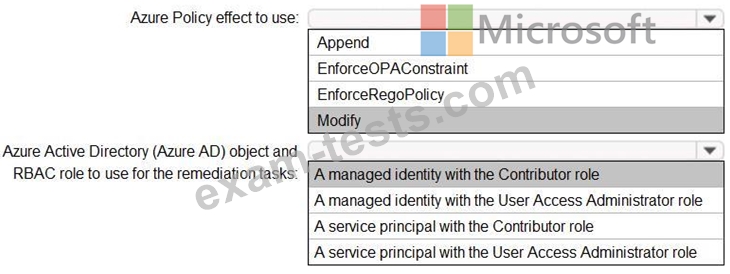
* For new resources, assign tags and values that match the tags and values of the resource group to which the resources are deployed.
* For existing resources, identify whether the tags and values match the tags and values of the resource group that contains the resources.
* For any non-compliant resources, trigger auto-generated remediation tasks to create missing tags and values.
The solution must use the principle of least privilege.
What should you include in the design? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question 52
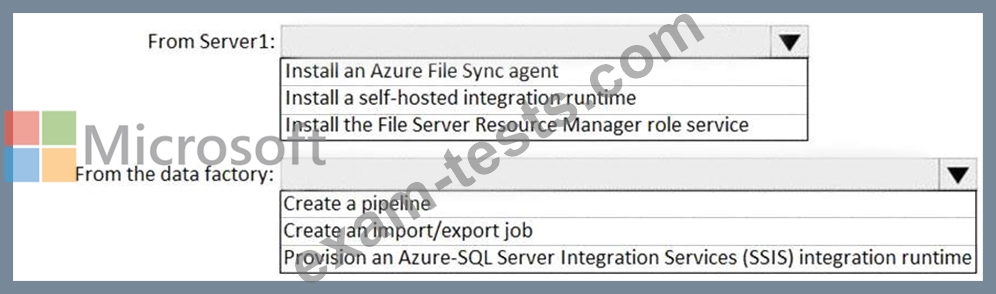
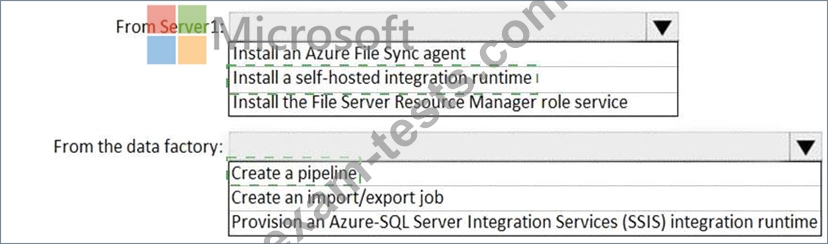
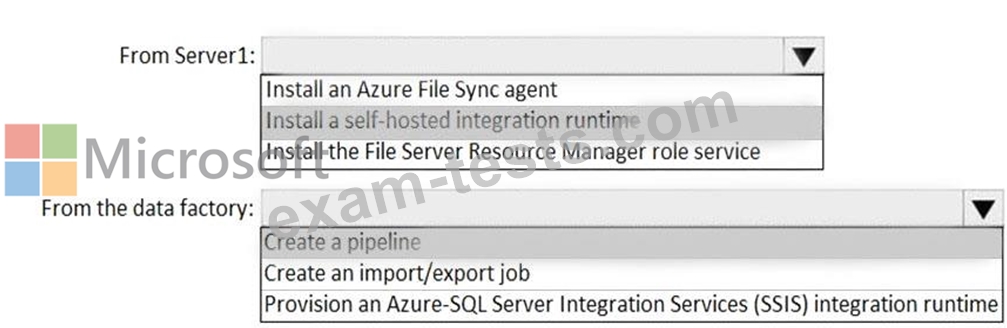
Your on-premises network contains a file server named Server1 that stores 500 GB of data.
You need to use Azure Data Factory to copy the data from Server1 to Azure Storage.
You add a new data factory.
What should you do next? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to use Azure Data Factory to copy the data from Server1 to Azure Storage.
You add a new data factory.
What should you do next? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question 53
Your company has 300 virtual machines hosted in a VMware environment. The virtual machines vary in size and have various utilization levels.
You plan to move all the virtual machines to Azure.
You need to recommend how many and what size Azure virtual machines will be required to move the current workloads to Azure. The solution must minimize administrative effort.
What should you use to make the recommendation?
You plan to move all the virtual machines to Azure.
You need to recommend how many and what size Azure virtual machines will be required to move the current workloads to Azure. The solution must minimize administrative effort.
What should you use to make the recommendation?
Question 54
You are designing a data protection strategy for Azure virtual machines. All the virtual machines use managed disks.
You need to recommend a solution that meets the following requirements:
* The use of encryption keys is audited.
* All the data is encrypted at rest always.
* You manage the encryption keys, not Microsoft.
What should you include in the recommendation?
You need to recommend a solution that meets the following requirements:
* The use of encryption keys is audited.
* All the data is encrypted at rest always.
* You manage the encryption keys, not Microsoft.
What should you include in the recommendation?
Question 55
Your company provides customer support for multiple Azure subscriptions and third-party hosting providers.
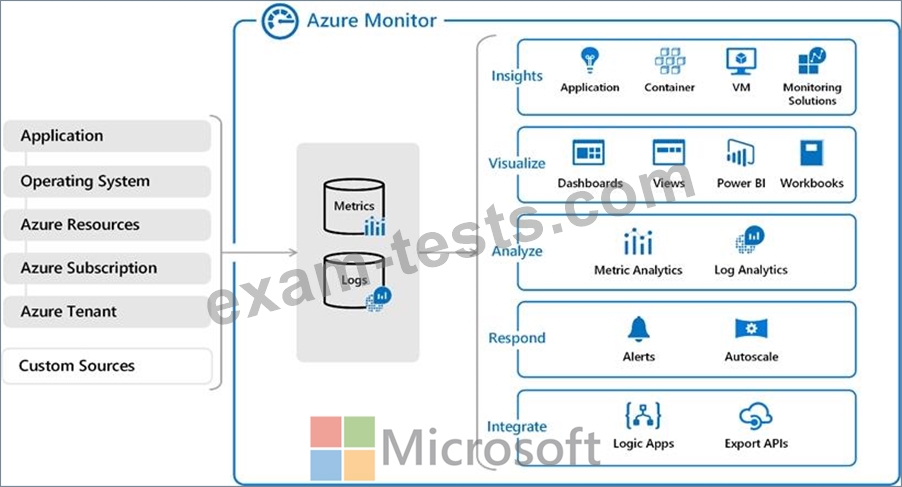
You are designing a centralized monitoring solution. The solution must provide the following services:
* Collect log and diagnostic data from all the third-party hosting providers into a centralized repository.
* Collect log and diagnostic data from all the subscriptions into a centralized repository.
* Automatically analyze log data and detect threats.
* Provide automatic responses to known events.
Which Azure service should you include in the solution?