

Question 131
4d 5a 90 00 03 00 00 00 04 00 00 00 ff ff 00 00 b8 00 00 00 00 00 00 00 40 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00 00
00 00 00 00 80 00 00 00 0e 1f ba 0e 00 b4 09 cd 21 b8 01 4c cd 21 54 68 69 73 20 70 72 6f 67 72 61 6d 20 63 61 6e 6e 6f 74 20 62 65 20 72 75 6e 20 69 6e 20 44 4f 53 20
6d 6f 64 65 2e 0d 0d 0a 24 00 00 00 00 00 00 00
50 45 00 00 4c 01 03 00 34 6d be 66 00 00 00 00 00 00 00 00 e0 00 0f 03 0b 01 05 00 00 70 00 00 00 10 00 00 00 d0 00 00 70 4c 01 00 00 e0 00 00 00 50 01 00 00 00 40 00
00 10 00 00 00 02 00 00 04 00 00 00 00 00 00 00 04 00 00 00 00 00 00 00 00 60 01 00 00 02 00 00 00 00 00 00 03 00 00 00 00 00 10 00 00 10 00 00 00 00 10 00 00 10 00 00
00 00 00 00 10 00 00 00 00 00 00 00 00 00 00 00
Attempts to run the code in a sandbox produce no results. Which of the following should the malware analyst do next to further analyze the malware and discover useful IoCs?
Question 132
An incident response team is analyzing malware and observes the following:
* Does not execute in a sandbox
* No network loCs
* No publicly known hash match
* No process injection method detected
Which of the following should the team do next to proceed with further analysis?
* Does not execute in a sandbox
* No network loCs
* No publicly known hash match
* No process injection method detected
Which of the following should the team do next to proceed with further analysis?
Question 133
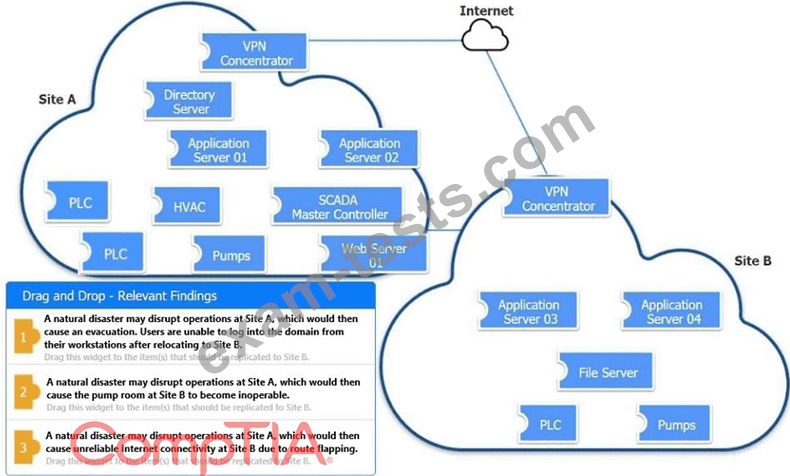

Question 134
Previously intercepted communications must remain secure even if a current encryption key is compromised in the future. Which of the following best supports this requirement?
Question 135
A security engineer needs 10 secure the OT environment based on me following requirements
* Isolate the OT network segment
* Restrict Internet access.
* Apply security updates two workstations
* Provide remote access to third-party vendors
Which of the following design strategies should the engineer implement to best meet these requirements?
* Isolate the OT network segment
* Restrict Internet access.
* Apply security updates two workstations
* Provide remote access to third-party vendors
Which of the following design strategies should the engineer implement to best meet these requirements?