

Question 111
After an incident response exercise, a security administrator reviews the following table:
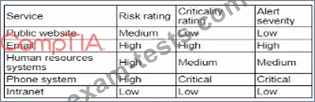
Which of the following should the administrator do to beat support rapid incident response in the future?
Which of the following should the administrator do to beat support rapid incident response in the future?
Question 112
A security analyst is reviewing suspicious log-in activity and sees the following data in the SICM:

Which of the following is the most appropriate action for the analyst to take?
Which of the following is the most appropriate action for the analyst to take?
Question 113
After a penetration test on the internal network, the following report was generated:

Which of the following should be recommended to remediate the attack?
Which of the following should be recommended to remediate the attack?
Question 114
A security architect wants to develop a baseline of security configurations These configurations automatically will be utilized machine is created Which of the following technologies should the security architect deploy to accomplish this goal?
Question 115
A security engineer is reviewing the SIEM logs after a server crashed. The following list of events represents the timeline of actions collected from the SIEM:
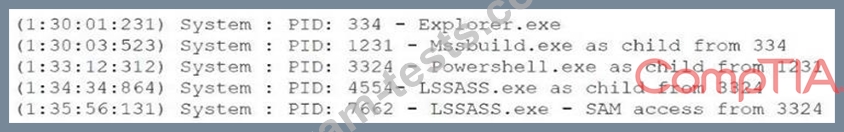
Which of the following TTPs is most likely associated with this SIEM log?
Which of the following TTPs is most likely associated with this SIEM log?