

Question 226
An enterprise is deploying APIs that utilize a private key and a public key to ensure the connection string is protected. To connect to the API, customers must use the private key. Which of the following would best secure the REST API connection to the database while preventing the use of a hard-coded string in the request string?
Question 227
A security engineer wants to enhance the security posture of end-user systems in a zero trust environment. Given the following requirements:
- Reduce the ability for potentially compromised endpoints to contact
C2 infrastructure.
- Track the requests that the malware makes to the IPs.
- Avoid the download of additional payloads.
Which of the following should the engineer deploy to meet these requirements?
- Reduce the ability for potentially compromised endpoints to contact
C2 infrastructure.
- Track the requests that the malware makes to the IPs.
- Avoid the download of additional payloads.
Which of the following should the engineer deploy to meet these requirements?
Question 228
An organization recently hired a third party to audit the information security controls present in the environment. After reviewing the audit findings, the Chief Information Security Officer (CISO) approved the budget for an in-depth defense strategy for network security. Which of the following is the most likely reason the CISO approved the additional budget?
Question 229
A security engineer is developing a solution to meet the following requirements?
* All endpoints should be able to establish telemetry with a SIEM.
* All endpoints should be able to be integrated into the XDR platform.
* SOC services should be able to monitor the XDR platform
Which of the following should the security engineer implement to meet the requirements?
* All endpoints should be able to establish telemetry with a SIEM.
* All endpoints should be able to be integrated into the XDR platform.
* SOC services should be able to monitor the XDR platform
Which of the following should the security engineer implement to meet the requirements?
Question 230
SIMULATION
[Security Architecture]
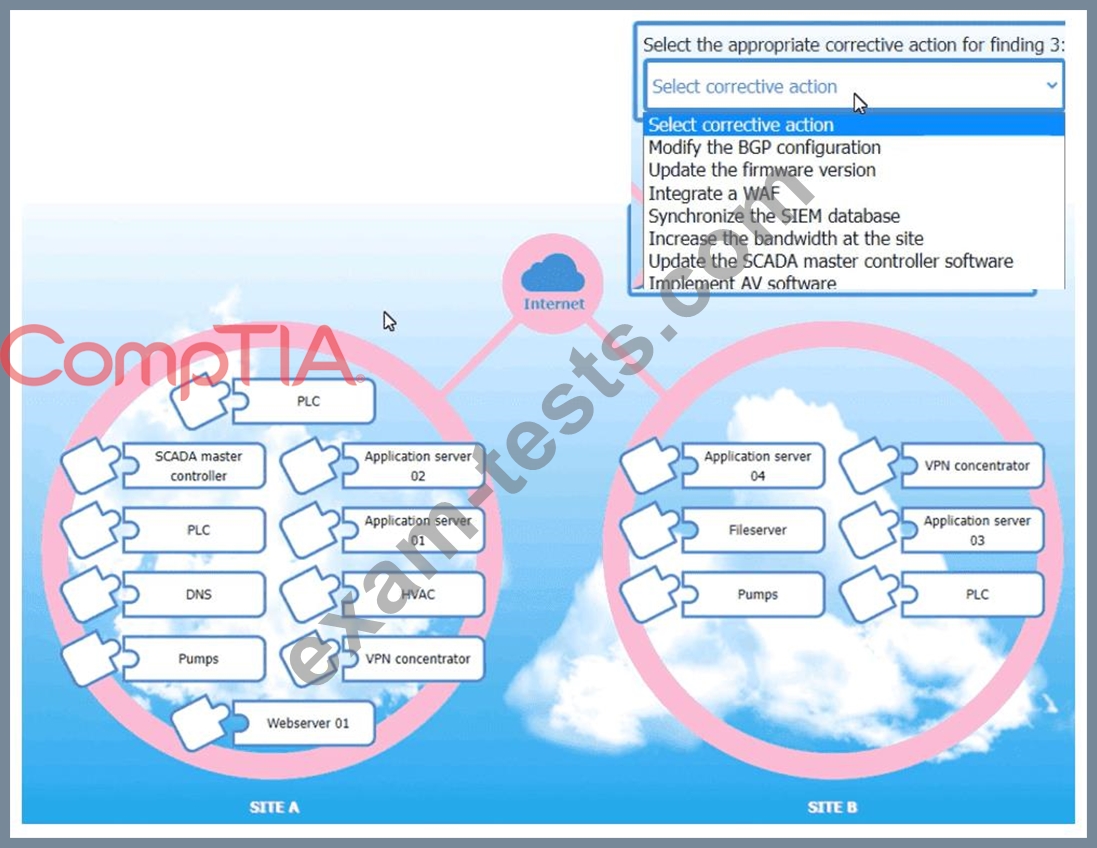
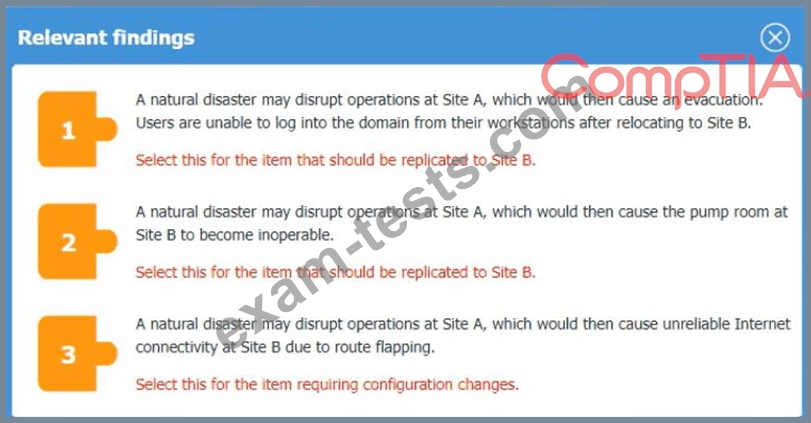
An organization is planning for disaster recovery and continuity ofoperations, and has noted the following relevant findings:
1. A natural disaster may disrupt operations at Site A, which would then cause an evacuation. Users are unable to log into the domain from-their workstations after relocating to Site B.
2. A natural disaster may disrupt operations at Site A, which would then cause the pump room at Site B to become inoperable.
3. A natural disaster may disrupt operations at Site A, which would then cause unreliable internet connectivity at Site B due to route flapping.
INSTRUCTIONS
Match each relevant finding to the affected host by clicking on the host name and selecting the appropriate number.
For findings 1 and 2, select the items that should be replicated to Site B. For finding 3, select the item requiring configuration changes, then select the appropriate corrective action from the drop-down menu.
[Security Architecture]
An organization is planning for disaster recovery and continuity ofoperations, and has noted the following relevant findings:
1. A natural disaster may disrupt operations at Site A, which would then cause an evacuation. Users are unable to log into the domain from-their workstations after relocating to Site B.
2. A natural disaster may disrupt operations at Site A, which would then cause the pump room at Site B to become inoperable.
3. A natural disaster may disrupt operations at Site A, which would then cause unreliable internet connectivity at Site B due to route flapping.
INSTRUCTIONS
Match each relevant finding to the affected host by clicking on the host name and selecting the appropriate number.
For findings 1 and 2, select the items that should be replicated to Site B. For finding 3, select the item requiring configuration changes, then select the appropriate corrective action from the drop-down menu.