

Question 231
A security engineer wants to stay up-to-date on new detections that are released on a regular basis. The engineer's organization uses multiple tools rather than one specific vendor security stack. Which of the following rule-based languages is the most appropriate to use as a baseline for detection rules with the multiple security tool setup?
Question 232
A company updates its cloud-based services by saving infrastructure code in a remote repository.
The code is automatically deployed into the development environment every time the code is saved lo the repository. The developers express concern that the deployment often fails, citing minor code issues and occasional security control check failures in the development environment.
Which of the following should a security engineer recommend to reduce the deployment failures?
(Select two).
Question 233
A company receives several complaints from customers regarding its website. An engineer implements a parser for the web server logs that generates the following output:
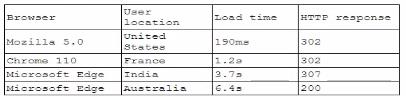
which of the following should the company implement to best resolve the issue?
which of the following should the company implement to best resolve the issue?
Question 234
A security administrator is reviewing the following code snippet from a website component:

A review of the inc.tmp file shows the following:

Which of the following is most likely the reason for inaccuracies?
A review of the inc.tmp file shows the following:
Which of the following is most likely the reason for inaccuracies?
Question 235
A security administrator is reviewing the following code snippet from a website component:

A review of the inc.tmp file shows the following:
Which of the following is most likely the reason for inaccuracies?
A review of the inc.tmp file shows the following:
Which of the following is most likely the reason for inaccuracies?