Question 36

Context
A project that you are working on has a requirement for persistent data to be available.
Task
To facilitate this, perform the following tasks:
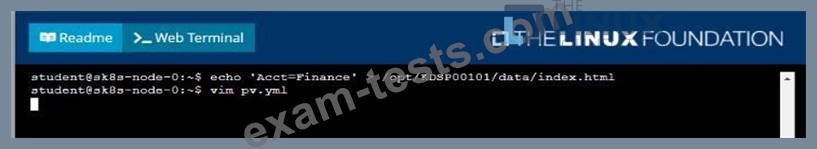
* Create a file on node sk8s-node-0 at /opt/KDSP00101/data/index.html with the content Acct=Finance
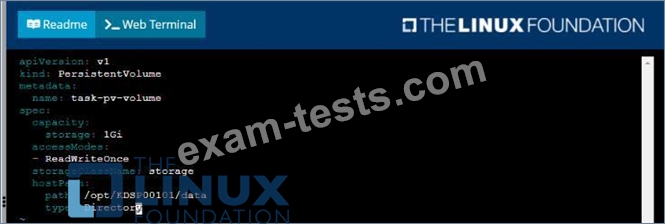
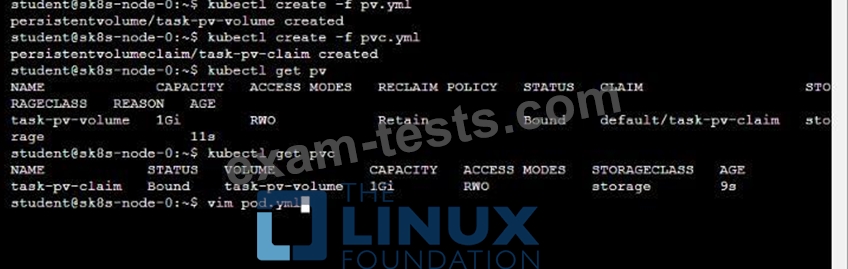
* Create a PersistentVolume named task-pv-volume using hostPath and allocate 1Gi to it, specifying that the volume is at /opt/KDSP00101/data on the cluster's node. The configuration should specify the access mode of ReadWriteOnce . It should define the StorageClass name exam for the PersistentVolume , which will be used to bind PersistentVolumeClaim requests to this PersistenetVolume.
* Create a PefsissentVolumeClaim named task-pv-claim that requests a volume of at least 100Mi and specifies an access mode of ReadWriteOnce
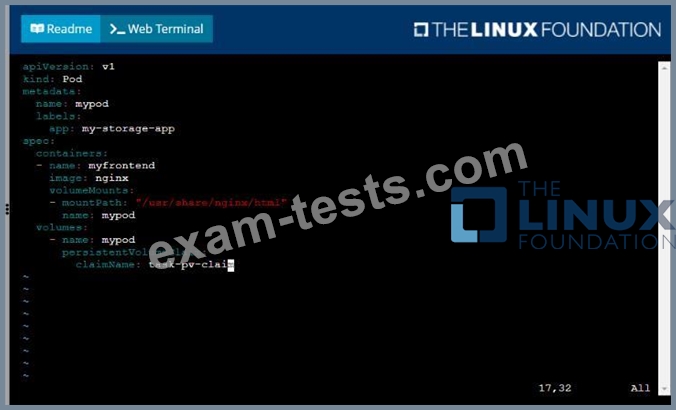
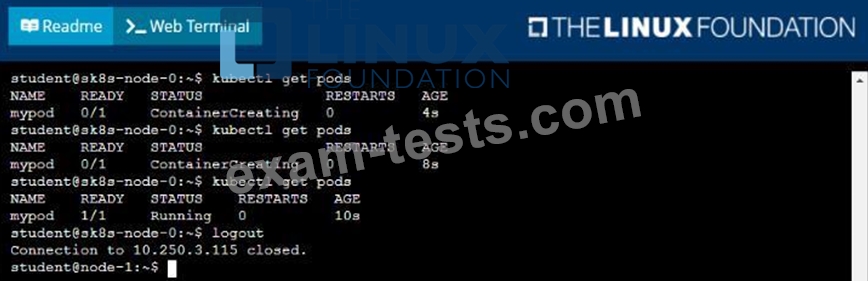
* Create a pod that uses the PersistentVolmeClaim as a volume with a label app: my-storage-app mounting the resulting volume to a mountPath /usr/share/nginx/html inside the pod

Question 37
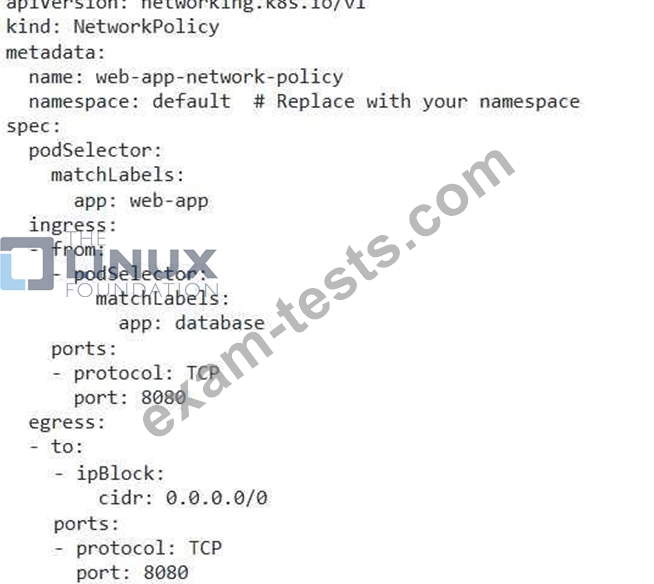
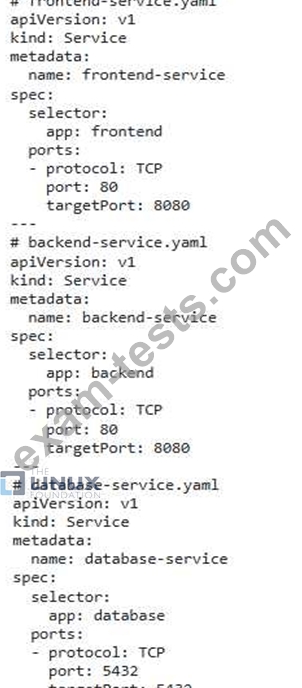
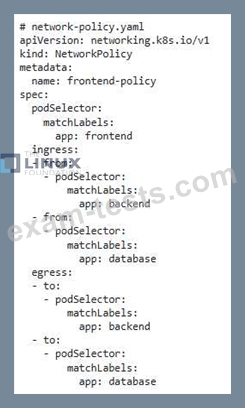
You are building a microservice application that consists of three components: a frontend service, a backend service, and a database service_ Each service is deployed as a separate pod in a Kubernetes cluster_ You need to implement health checks for each service to ensure that the application remains healthy and available. The frontend service should be able to reach both the backend service and the database service successfully. How would you implement health checks using Kustomize and ensure that the trontend service can only access the backend service and the database service within the cluster?

Question 38
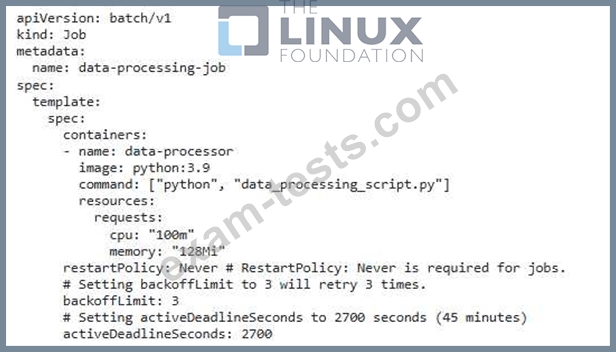
You have a Kubernetes Job that runs a Python script for data processing. The script takes 30 minutes to complete, and you need to ensure that the Job is retried up to 3 times if it fails. Additionally, you want the Job to complete within a maximum of 45 minutes. Create a Job YAML file with appropriate configuration.
Question 39

Task:
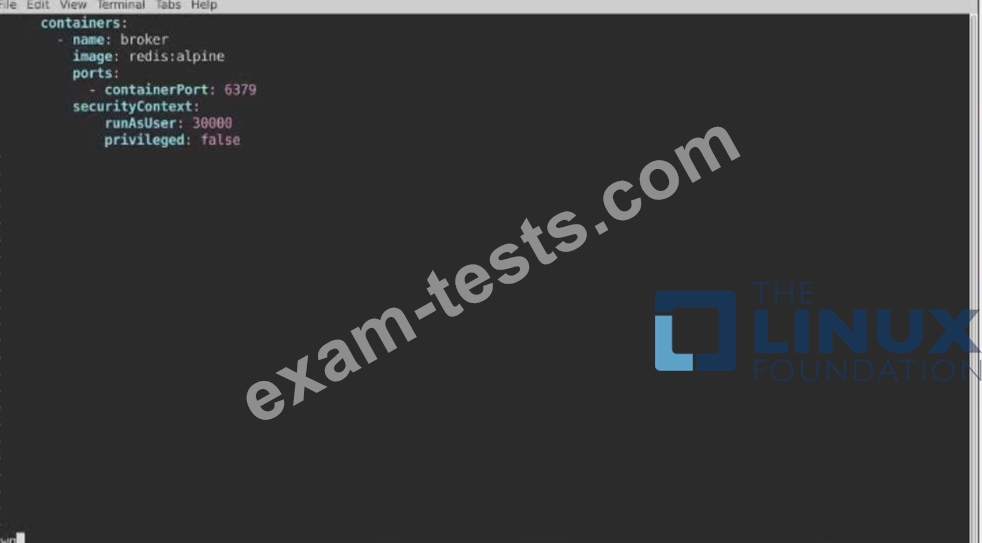
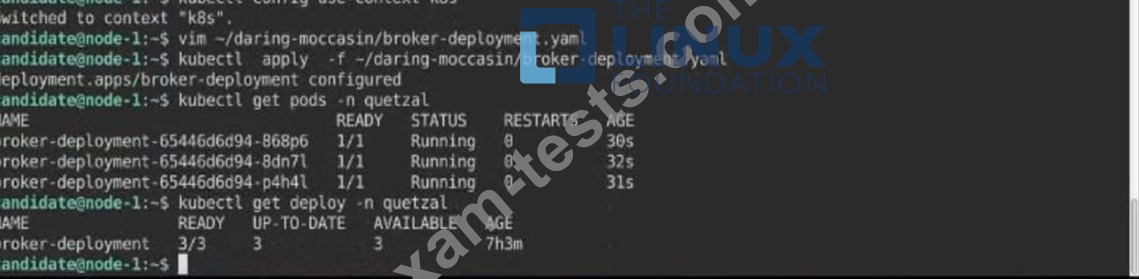
Modify the existing Deployment named broker-deployment running in namespace quetzal so that its containers.
1) Run with user ID 30000 and
2) Privilege escalation is forbidden
The broker-deployment is manifest file can be found at:

Question 40
You are running a web application in a Kubernetes cluster. You have a deployment named 'web- app' with two replicas. You need to implement a Network Policy that allows only traffic from pods with the label app: database' to access the 'web-app' deployment on port 8080. You also need to block all other traffic to the 'web-app' deployment.