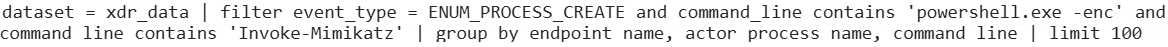A global enterprise has implemented Cortex XSIAM and is ingesting logs from various sources, including endpoint sensors (XDR agents), network firewalls, cloud infrastructure (AWS CloudTrail, Azure Activity Logs), and identity providers (Okta). The security team observes that while basic event correlation is working, the fidelity of stitched incidents involving cloud and on-premise interactions is lower than expected. Specifically, the XSIAM 'Incident View' often shows separate alerts for related activities (e.g., a user logging into Okta, then an EC2 instance, then a suspicious file access on an on-premise server) rather than a unified attack story. Which of the following is the MOST likely root cause for this reduced stitching fidelity, and what configuration adjustment within XSIAM could address it?
Correct Answer: C
This is a common challenge in large, hybrid environments. Log Stitching relies heavily on identifying common attributes to link events. If a user's identity is '[email protected]' in Okta, 'jdoe' in AWS, and 'JOHN_D' on an on-premise server, XSIAM's stitching engine will struggle to connect these activities as belonging to the same entity unless these different formats are normalized or mapped to a single canonical identity. Similarly, consistent asset tagging or unique session IDs across environments are crucial. Therefore, the most likely root cause is inconsistent or missing common identifiers. Implementing robust 'Data Normalization Rules' (to parse and format data consistently) and 'Attribute Mapping' (to map different representations of the same entity to a canonical form) within XSIAM's data ingestion pipeline is the critical configuration adjustment to improve stitching fidelity for such cross-environment scenarios.
Question 57
An advanced persistent threat (APT) actor attempts to maintain persistence on a compromised system by modifying a legitimate system service's configuration to execute a malicious script at startup. The script itself is polymorphic and changes its hash frequently, bypassing signature-based detection. Which Cortex XDR sensor component is designed to detect and prevent this specific type of persistence mechanism, even with the polymorphic nature of the script?
Correct Answer: D
The key here is 'polymorphic' and 'persistence mechanism'. Signature-based (A) and cloud analysis (B) might struggle with polymorphism. Anti-Tampering (C) protects Cortex XDR itself. Network Protection (E) is reactive. The Behavioral Threat Protection (BTP) engine is designed to detect anomalous system behavior, including modifications to legitimate system services, registry keys, and other common persistence mechanisms. It focuses on the 'how' (the action of modifying a service) rather than the 'what' (the specific hash of the malicious script), making it effective against polymorphic or fileless persistence attempts. This is a core strength of BTP in detecting advanced threats.
Question 58
Which activities are facilitated through the War Room in Cortex XSOAR? (Choose one answer)
Correct Answer: A
The War Room in Cortex XSOAR is the primary collaborative workspace where analysts interact with an incident in real-time. It acts as a digital "command center" for the investigation. * CLI and Command Execution: The most defining feature of the War Room is the command-line interface (CLI) at the bottom. This allows analysts to run scripts and integration commands (e.g., !ad- disable-user or !vt-get-url) directly. * Collaboration: It provides a central log of every action taken. When multiple analysts work on a single incident, they can see each other's commands, notes, and the outputs of automated tasks, similar to a chat application but enriched with security data. * Evidence Collection: Every command run and every result returned in the War Room can be marked as evidence, which is then automatically compiled into the final incident report. Why other options are incorrect: * Option B: Managing the "to-do" list of an incident (creating/editing tasks) is done in the Workplan tab. * Option C: High-level overviews and summaries are found in the Incident Info or Dashboards views. * Option D: While investigation happens here, "initial investigation" is usually a function of the Classification and Mapping phase or the Incident Summary view before an analyst dives into the manual command execution of the War Room.
Question 59
During the 'Recovery' phase of the NIST Incident Response Plan, after a data exfiltration incident, a SOC analyst needs to ensure the integrity of critical data and systems before bringing them back online. Which of the following technical validation steps, incorporating Palo Alto Networks capabilities, is crucial for a robust recovery and prevents re-infection?
Correct Answer: C
The 'Recovery' phase involves restoring affected systems and services. Option C is key for robust recovery and preventing re- infection. Simply restoring from backup (A) doesn't guarantee the backup itself wasn't compromised or that new malware wasn't introduced during recovery. Using Cortex XDR's post-infection analysis for residual threats and correlating with WildFire verdicts ensures that restored systems are clean from known and potentially new (zero-day) malware, providing a high level of confidence before full reintegration. Blocking all outbound traffic (B) is too restrictive for recovery, and user training is for prevention. Pinging servers (D) is a basic availability check, not a security validation. Implementing a completely new network architecture (E) is an extreme and often impractical step for most recovery scenarios.
Question 60
Consider the following Cortex XDR KQL query used by a security analyst: This query is attempting to identify instances of PowerShell being used for credential dumping. From a behavioral analytics perspective, what is the primary limitation of relying solely on such a KQL query for detecting advanced persistent threats (APTs) that often leverage living-off-the-land (LOTL) techniques?
Correct Answer: B
While options A and D highlight valid limitations of this specific query in a broader context, the primary limitation from a behavioral analytics perspective, especially for APTs and LOTL, is its susceptibility to obfuscation (Option B). Attackers frequently encode, encrypt, or otherwise modify PowerShell commands (e.g., using different encoding schemes, character manipulation, or entirely different tools) to evade simple string-based detections like 'Invoke-Mimikatz'. Behavioral analytics in Cortex XDR goes beyond such static string matching, looking for the intent and sequence of actions, regardless of the exact command line, making it more resilient to obfuscation. While PowerShell is legitimate (Option C), the combination with 'Invoke-Mimikatz' makes it suspicious. The query does access historical data (Option E) and could be part of a real-time detection rule (not inherently limited to historical). Option A and D are true, but not the primary limitation in the context of behavioral evasion.
Newest SecOps-Pro Exam PDF Dumps shared by BraindumpsPass.com for Helping Passing SecOps-Pro Exam! BraindumpsPass.com now offer the updated SecOps-Pro exam dumps, the BraindumpsPass.com SecOps-Pro exam questions have been updated and answers have been corrected get the latest BraindumpsPass.com SecOps-Pro pdf dumps with Exam Engine here: