Your organization has just implemented a new cloud-native application, and threat intelligence suggests a surge in attacks targeting misconfigurations in similar cloud environments, specifically related to IAM roles and API key exposure. Palo Alto Networks Prisma Cloud is deployed. How can the incident response team proactively leverage this threat intelligence within Prisma Cloud to prevent potential security incidents, moving beyond basic posture management to active threat detection and response?
Correct Answer: B
This question focuses on leveraging threat intelligence proactively within a cloud security posture management (CSPM) and cloud workload protection platform (CWPP) like Prisma Cloud, moving beyond simple detection to preventative and automated measures. Option B (Custom RQL rules + CIICD integration): This is the most effective proactive approach: Custom RQL rules: RQL is Prisma Cloud's powerful query language for identifying specific resource configurations and relationships. Leveraging threat intelligence (e.g., common misconfigurations, patterns of overly permissive policies) to write precise RQL rules allows the organization to actively scan their cloud environment for these exact vulnerabilities. CIICD pipeline integration: Integrating these RQL checks into the CI/CD pipeline (e.g., via Prisma Cloud's lac security capabilities) ensures that misconfigured IAM roles or exposed API keys are detected before deployment, effectively preventing the incident from occurring in production. This is 'shift-left security' in action, directly driven by intelligence on adversary TTPs. Let's analyze why other options are less optimal: A: Automatic remediation of 'AdministratorAccess' (while good in principle) can be too broad and disruptive without granular control or context from specific threat intelligence. Disabling exposed API keys is reactive. C: Manual review is not scalable or rapid enough for proactive prevention in dynamic cloud environments. Automation is key. D: Prisma Cloud's Network Protection is for network-level traffic inspection, which is valuable but doesn't directly address the misconfiguration of IAM roles and API keys, which is the initial attack vector highlighted by the threat intelligence. E While subscribing to feeds is good, the question asks how the incident response team leverages this intelligence proactively for prevention. A generic feed subscription doesn't describe the specific actions taken to translate that intelligence into proactive security controls like custom RQL rules or CI/CD integration.
Question 2
Where in Cortex XSOAR are analysts able to collaborate and converse with others for joint real-time investigations?
Correct Answer: B
The War Room is the central collaborative feature of Cortex XSOAR. It is designed to mimic a physical "war room" where security experts gather to solve a crisis. * Real-Time Collaboration: It features a chat-like interface where analysts can post notes, upload files, and tag other team members to collaborate on a specific incident in real-time. * Shared CLI: Every analyst in the War Room sees the commands being run by others and the results of those commands. This prevents duplication of effort and ensures everyone has the same context. * Note on Evidence Board (C): While the Evidence Board displays captured artifacts, the conversation and collaboration happen exclusively within the War Room interface. * Correction: Corrected "analystsle" to "analysts are able."
Question 3
During a Red Team exercise, a penetration tester successfully evades initial detection by using living-off-the-land binaries (LoLBins) and polymorphic malware. The activities include rund1132 .exe executing a malicious DLL, followed by certutil. exe for data download, and then schtasks . exe to establish persistence. No single activity triggers a high-severity alert. Which of the following Log Stitching and analysis principles within Cortex XDR would be most instrumental in identifying this attack chain as a unified incident?
Correct Answer: C
LoLBins and polymorphic malware are designed to evade signature-based detection (A) and often appear as normal system activity when viewed in isolation (B). Manual correlation (E) is inefficient and prone to human error at scale. Deep packet inspection (D) is valuable but won't capture the full endpoint-level execution chain. The power of Cortex XDR's Log Stitching against such sophisticated attacks lies in its integration with advanced Behavioral Analytics and ML (C). These engines identify subtle, anomalous behaviors (e.g., rund1132. exe behaving unusually, certutil . exe downloading from suspicious URLs, schtasks . exe creating unusual tasks). Log Stitching then connects these 'dots' based on their causal relationships (e.g., rund1132 leading to certutil leading to schtasks ), shared host/user context, and temporal proximity, culminating in a single, high-fidelity incident that reveals the entire attack. This is fundamental for detecting attacks that 'live off the land'.
Question 4
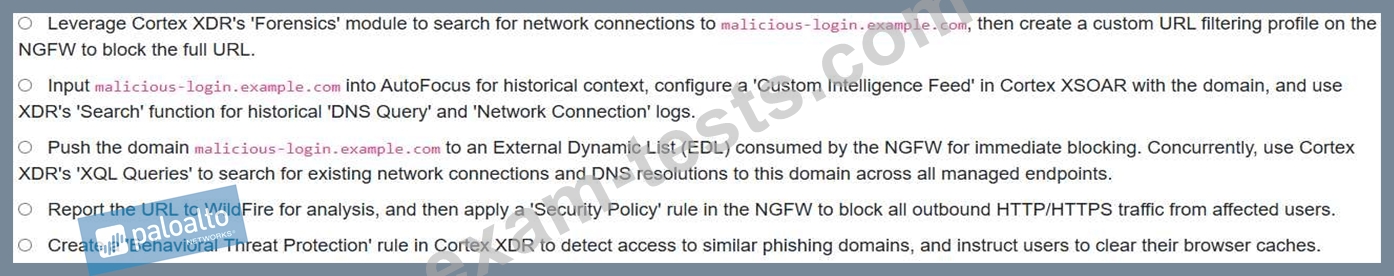
A phishing email campaign successfully targets several employees, leading to credential harvesting. The email contained a malicious link to hxxps : //malicious-login.example.com/authenticate.php. A SOC analyst wants to use Cortex products to proactively prevent further access to this domain and associated URLs, and to identify any endpoints that might have already accessed it. Which combination of Cortex capabilities would achieve this most effectively?
Correct Answer: C
Option C is the most effective and comprehensive approach. EDLs are highly efficient for dynamic blocking of domains on NGFWs, providing immediate network-wide prevention. Simultaneously, Cortex XDR's XQL (Cortex Query Language) allows for powerful historical searches across endpoint telemetry (DNS, network connections) to identify past access. Option A's URL filtering profile might be too granular for the whole domain and 'Forensics' might not be the most efficient for broad search. Option B is good for enrichment and feed creation but doesn't explicitly cover the immediate blocking or comprehensive historical search as effectively. Option D is too broad and would disrupt legitimate traffic. Option E is reactive and relies on user action, and 'Behavioral Threat Protection' might not catch a simple, direct access to a known malicious domain as efficiently as direct blocking and XQL querying.
Question 5
Consider a Palo Alto Networks Cortex XDR deployment aiming for proactive threat hunting. An analyst observes an alert from Cortex XDR indicating 'Lateral Movement - Anomalous Process Creation' with a confidence score of 85%. Upon investigation, it's determined to be a legitimate administrator activity. How does the distinction between Machine Learning (ML) and Artificial Intelligence (AI) influence the system's ability to adapt and refine such alerts, and what specific Palo Alto Networks feature exemplifies this AI capability?
Correct Answer: B
While ML models can be retrained (A), the 'AI' aspect goes beyond simple model updates. Option B correctly identifies that AI, particularly when integrated with UBA and identity context, allows for a higher-level understanding of user 'intent' and 'normal behavior' for specific entities. This enables the system to proactively adjust its risk scoring and alert generation for similar future legitimate activities without explicit, manual retraining cycles for every new benign pattern. Palo Alto Networks' behavioral analytics, often powered by AI, learns and adapts to specific user and entity behaviors, which is key here. Option C is less accurate as autonomous rule generation for every benign activity is not standard, and D is about explanation, not adaptation. E trivializes the distinction.