

Question 306
A security engineer deploys an enterprise-wide host/endpoint technology for all of the company's corporate PCs. Management requests the engineer to block a selected set of applications on all PCs.
Which technology should be used to accomplish this task?
Which technology should be used to accomplish this task?
Question 307
Which type of data must an engineer capture to analyze payload and header information?
Question 308
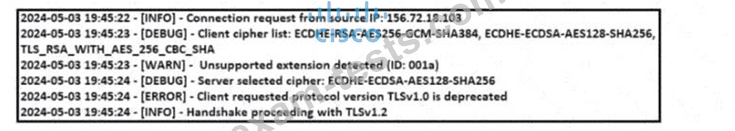
Refer to the exhibit Which TLS version does this client support?
Question 309
What is a difference between an inline and a tap mode traffic monitoring?
Question 310
After a large influx of network traffic to externally facing devices, a security engineer begins investigating what appears to be a denial of service attack When the packet capture data is reviewed, the engineer notices that the traffic is a single SYN packet to each port Which type of attack is occurring?