

Question 296
Which action matches the weaponization step of the Cyber Kill Chain Model?
Question 297
A suspicious user opened a connection from a compromised host inside an organization. Traffic was going through a router and the network administrator was able to identify this flow. The admin was following 5- tuple to collect needed data. Which information was gathered based on this approach?
Question 298
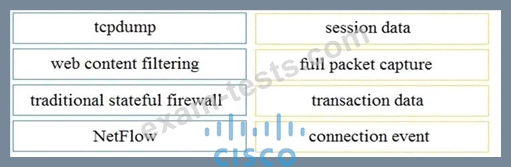
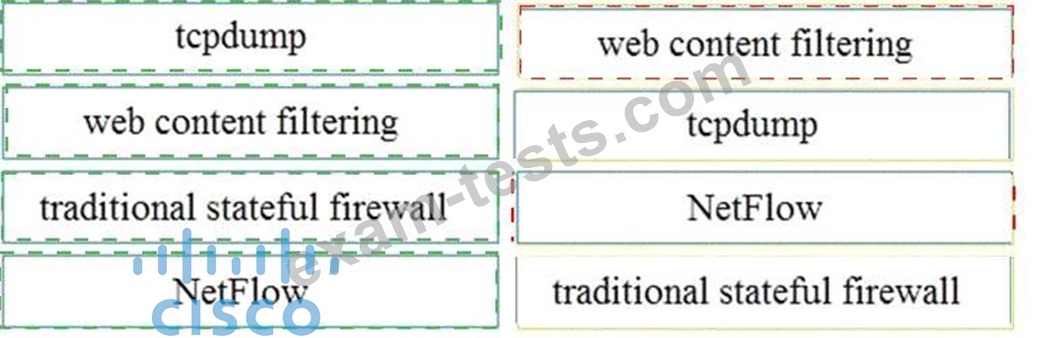
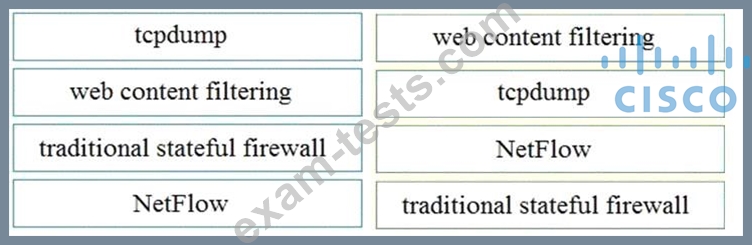
Drag and drop the technology on the left onto the data type the technology provides on the right.
Question 299
A malicious file has been identified in a sandbox analysis tool.
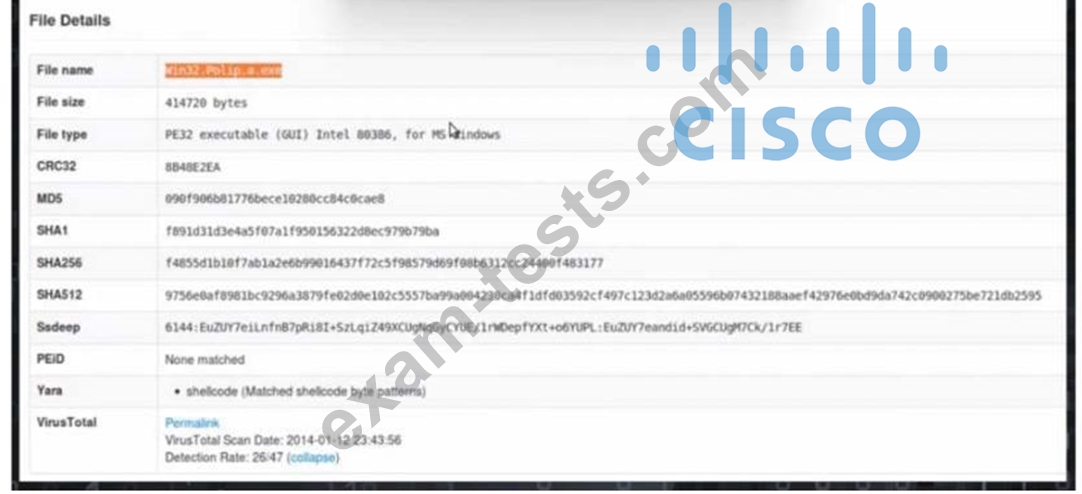
Which piece of information is needed to search for additional downloads of this file by other hosts?
Which piece of information is needed to search for additional downloads of this file by other hosts?
Question 300
Which information must an organization use to understand the threats currently targeting the organization?