

Question 96
An incident response team is analyzing malware and observes the following:
- Does not execute in a sandbox
- No network loCs
- No publicly known hash match
- No process injection method detected
Which of the following should the team do next to proceed with further analysis?
- Does not execute in a sandbox
- No network loCs
- No publicly known hash match
- No process injection method detected
Which of the following should the team do next to proceed with further analysis?
Question 97
A company experienced a data breach, resulting in the disclosure of extremely sensitive data regarding a merger. As a regulated entity, the company must comply with reporting and disclosure requirements. The company is concerned about its public image and shareholder values. Which of the following best supports the organization in addressing its concerns?
Question 98
A security analyst is troubleshooting the reason a specific user is having difficulty accessing company resources The analyst reviews the following information:
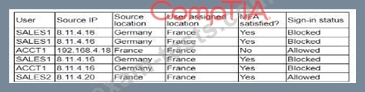
Which of the following is most likely the cause of the issue?
Which of the following is most likely the cause of the issue?
Question 99
A SOC analyst must perform threat-modeling activities for a large media organization that has the following characteristics:
* The organization maintains operations around the world in support of multiple entertainment networks.
* Development activities for the organization ' s web-based platforms occur overseas.
* Previous information security failures within the organization have been publicly disclosed.
Which of the following actions is the best for the analyst to consider in the early phases of threat modeling?
Question 100
During a gap assessment, an organization notes that OYOD usage is a significant risk. The organization implemented administrative policies prohibiting BYOD usage However, the organization has not implemented technical controls to prevent the unauthorized use of BYOD assets when accessing the organization's resources.
Which of the following solutions should the organization implement to better reduce the risk of BYOD devices? (Select two).
Which of the following solutions should the organization implement to better reduce the risk of BYOD devices? (Select two).