

Question 101
After several companies in the financial industry were affected by a similar incident, they shared information about threat intelligence and the malware used for exploitation. Which of the following should the companies do to best indicate whether the attacks are being conducted by the same actor?
Question 102
During a forensic review of a cybersecurity incident, a security engineer collected a portion of the payload used by an attacker on a comprised web server Given the following portion of the code:
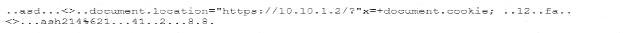
Which of the following best describes this incident?
Which of the following best describes this incident?
Question 103
A company needs to create a design that facilitates monitoring and alerting over the identity and access management surface. A primary design consideration should be the existence of multiple independent identity providers with a hybrid, multicloud environment. Which of the following components should be included as part of the design?
Question 104
Audit findings indicate several user endpoints are not utilizing full disk encryption. During me remediation process, a compliance analyst reviews the testing details for the endpoints and notes the endpoint device configuration does not support full disk encryption. Which of the following is the most likely reason me device must be replaced?
Question 105
To prevent data breaches, security leaders at a company decide to expand user education to:
* Create a healthy security culture.
* Comply with regulatory requirements.
* Improve incident reporting.
Which of the following would best meet their objective?
* Create a healthy security culture.
* Comply with regulatory requirements.
* Improve incident reporting.
Which of the following would best meet their objective?