

Question 41
You are an experienced ISMS audit team leader providing instruction to a class of auditors in training. The subject of today's lesson is the management of information security risk in accordance with the requirements of ISO/IEC 27001:2022.
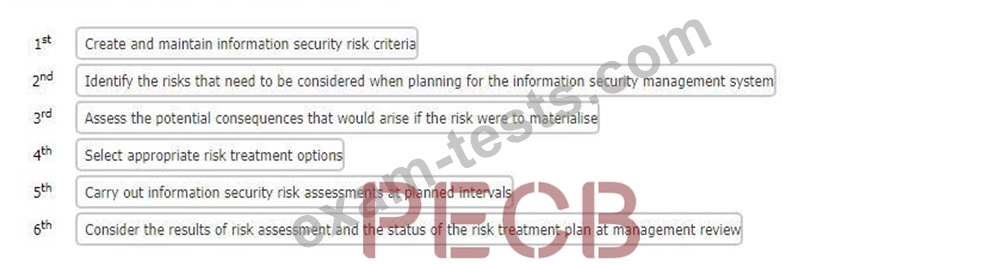
You provide the class with a series of activities. You then ask the class to sort these activities into the order in which they appear in the standard.
What is the correct sequence they should report back to you?
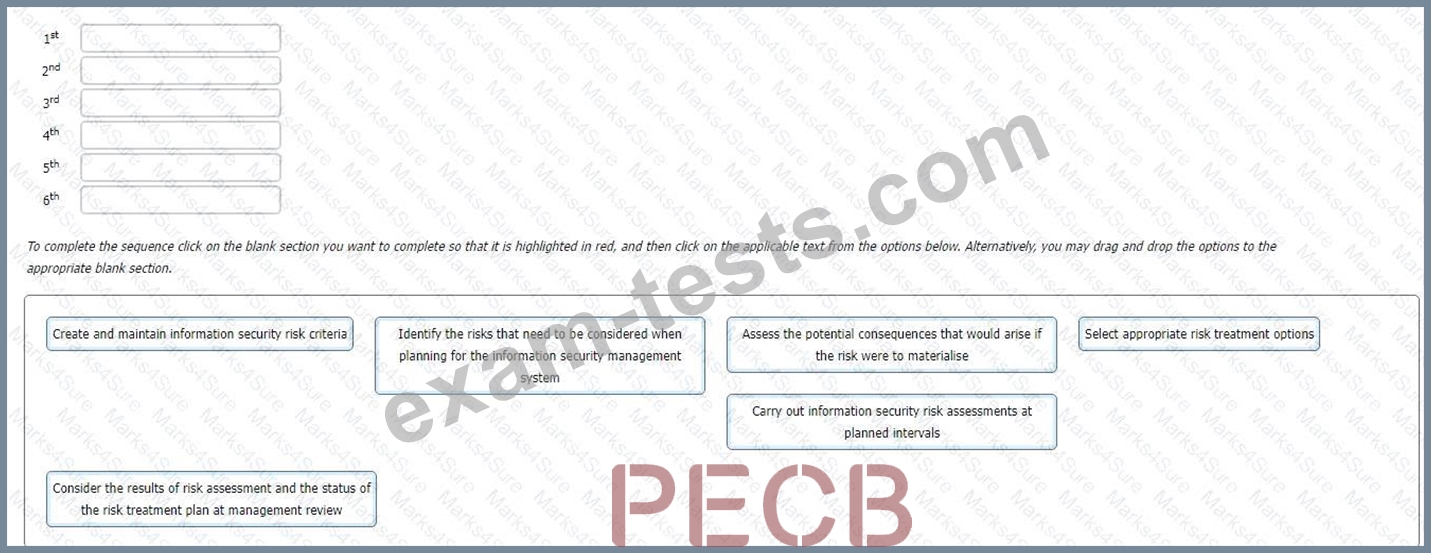
You provide the class with a series of activities. You then ask the class to sort these activities into the order in which they appear in the standard.
What is the correct sequence they should report back to you?
Question 42
You are performing an ISMS audit at a residential nursing home called ABC that provides healthcare services.
You find all nursing home residents wear an electronic wristband for monitoring their location, heartbeat, and blood pressure always. You learned that the electronic wristband automatically uploads all data to the artificial intelligence (AI) cloud server for healthcare monitoring and analysis by healthcare staff.
To verify the scope of ISMS, you interview the management system representative (MSR) who explains that the ISMS scope covers an outsourced data center.
Select one option of the correct statement which defines the content of the scope of the ISMS.
Question 43
You are an experienced ISMS audit team leader guiding an auditor in training. Your team has just completed a third-party surveillance audit of a mobile telecom provider. The auditor in training asks you how you intend to prepare for the Closing meeting. Which four of the following are appropriate responses?
Question 44
You work in the office of a large company. You receive a call from a person claiming to be from the Helpdesk. He asks you for your password.
What kind of threat is this?
What kind of threat is this?
Question 45
Which two of the following phrases would apply to 'check' in the Plan-Do-Check-Act cycle for a business process?
Premium Bundle
Newest ISO-IEC-27001-Lead-Auditor Exam PDF Dumps shared by BraindumpsPass.com for Helping Passing ISO-IEC-27001-Lead-Auditor Exam! BraindumpsPass.com now offer the updated ISO-IEC-27001-Lead-Auditor exam dumps, the BraindumpsPass.com ISO-IEC-27001-Lead-Auditor exam questions have been updated and answers have been corrected get the latest BraindumpsPass.com ISO-IEC-27001-Lead-Auditor pdf dumps with Exam Engine here: