

Question 31
The following are purposes of Information Security, except:
Question 32
You are conducting an ISMS audit in the despatch department of an international logistics organisation that provides shipping services to large organisations including local hospitals and government offices. Parcels typically contain pharmaceutical products, biological samples, and documents such as passports and driving licences. You note that the company records show a very large number of returned items with causes including mis-addressed labels and, in 15% of company cases, two or more labels for different addresses for the one package. You are interviewing the Shipping Manager (SM).
You: Are items checked before being dispatched?
SH: Any obviously damaged items are removed by the duty staff before being dispatched, but the small profit margin makes it uneconomic to implement a formal checking process.
You: What action is taken when items are returned?
SM: Most of these contracts are relatively low value, therefore it has been decided that it is easier and more convenient to simply reprint the label and re-send individual parcels than it is to implement an investigation.
You raise a nonconformity. Referencing the scenario, which six of the following Appendix A controls would you expect the auditee to have implemented when you conduct the follow-up audit?
Question 33
What is social engineering?
Question 34
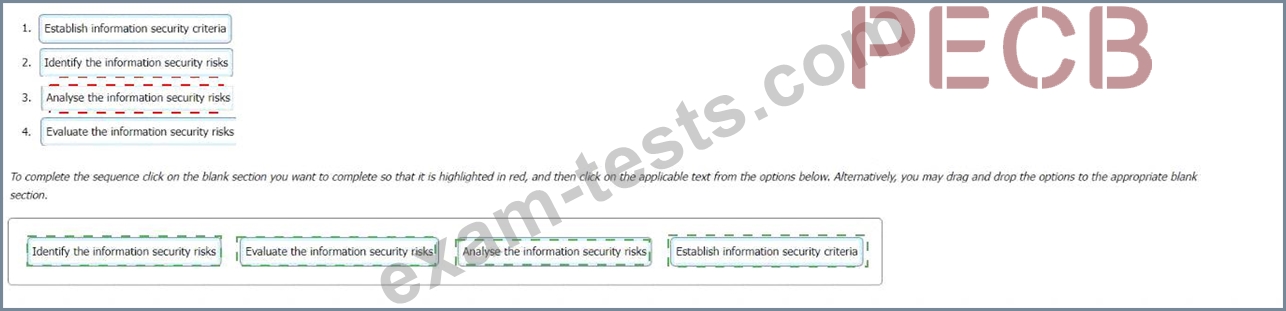
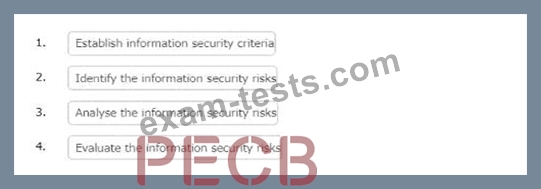
Select the correct sequence for the information security risk assessment process in an ISMS.
To complete the sequence click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the options to the appropriate blank
To complete the sequence click on the blank section you want to complete so that it is highlighted in red, and then click on the applicable text from the options below. Alternatively, you may drag and drop the options to the appropriate blank
Question 35
You are performing an ISMS audit at a residential nursing home railed ABC that provides healthcare services.
The next step in your audit plan is to verify the effectiveness of the continual improvement process. During the audit, you learned most of the residents' family members (90%) receive WeCare medical device promotional advertisements through email and SMS once a week via ABC's healthcare mobile app. All of them do not agree on the use of the collected personal data (or marketing or any other purposes than nursing and medical care on the signed service agreement with ABC. They have very strong reason to believe that ABC is leaking residents' and family members' personal information to a non-relevant third party and they have filed complaints.
The Service Manager says that all these complaints have been treated as nonconformities, and the corrective actions have been planned and implemented according to the Nonconformity and Corrective management procedure. The corrective action involved stopping working with WeCare the medical device manufacturer immediately and asking them to delete all personal data received as well as sending an apology email to all residents and their family members.
You are preparing the audit findings. Select one option of the correct finding.