

Question 41
You have a Microsoft 365 subscription that contains 20 data loss prevention (DLP) policies.
You need to identify the following:
*Rules that are applied without triggering a policy alert
*The top 10 files that have matched DLP policies
*Alerts that are miscategorized
Which report should you use for each requirement? To answer, drag the appropriate reports to the correct requirements. Each report may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.

Question 42
Hotspot Question
You have a Microsoft 365 E5 subscription that contains a user named User1.
You deploy Microsoft Purview Data Security Posture Management for AI (DSPM for AI).
You need to ensure that User1 can perform the following actions:
- View recommendations from the Recommendations page.
- View the user risk level for all events by using Activity explorer.
The solution must follow the principle of least privilege.
To which role group should you add User1 for each action? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Question 43
You have a Microsoft 365 E5 subscription.
You plan to use insider risk management to collect and investigate forensic evidence.
You need to enable forensic evidence capturing.
What should you do first?
You plan to use insider risk management to collect and investigate forensic evidence.
You need to enable forensic evidence capturing.
What should you do first?
Question 44
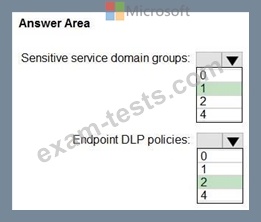
Hotspot Question
You have a Microsoft 365 E5 subscription.
You need to implement Endpoint data loss prevention (Endpoint DLP) to meet the following requirements:
- Ensure that users can upload data to only two sites named Site1 and
Site2.
- Prevent users from pasting data to two search engines named Search1
and Search2.
- Minimize the number of policies and groups.
What is the minimum number of sensitive service domain groups and Endpoint DLP policies required? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question 45
You are planning a data loss prevention (DLP) solution that will apply to Windows Client computers.
You need to ensure that when users attempt to copy a file that contains sensitive information to a USB storage device, the following requirements are met:
*If the users are members of a group named Group1, the users must be allowed to copy the file, and an event must be recorded in the audit log.
*All other users must be blocked from copying the file.
What should you create?